Set up custom OAuth applications for integrations, assign clients to your workspace or user groups, and control scopes, tenant policies, and branding.
You can use multiple custom OAuth clients for the same integration. Set one client for your entire workspace, offer User choice clients that members pick before they connect, or assign clients to specific user groups.
When you configure a custom OAuth client, Langdock routes new authentication flows through your OAuth application instead of the default Langdock client. A workspace client applies by default, and a group client applies to members of its groups. User choice is available for OAuth integrations, including built-in integrations. It is not available for MCP servers, OAuth 2.0 (Dynamic Client Registration), or OAuth 2.0 (CIMD). When any User choice client is active, members choose a client before they connect, and that choice takes priority over the workspace client and group clients. This means:
Your branding (custom name and logo) appears in consent screens
Your tenant policies control user access and admin consent requirements
Your rate limits apply to API calls made by your users
Your user groups can authenticate through separate OAuth clients
1
Create OAuth App at Provider
Register a new OAuth application in your provider’s developer portal (Google Cloud Console, Microsoft Azure, etc.).Required Configuration:
Copy the exact redirect URL from Langdock’s integration settings
Select all required scopes shown in Langdock for that integration
Configure any tenant-specific settings (admin consent, allowlisting)
2
Gather Credentials
Note down the following from your OAuth app:
Client ID (always required)
Client secret (required for most integrations)
Tenant ID (optional, shown for Microsoft integrations only)
3
Configure in Langdock
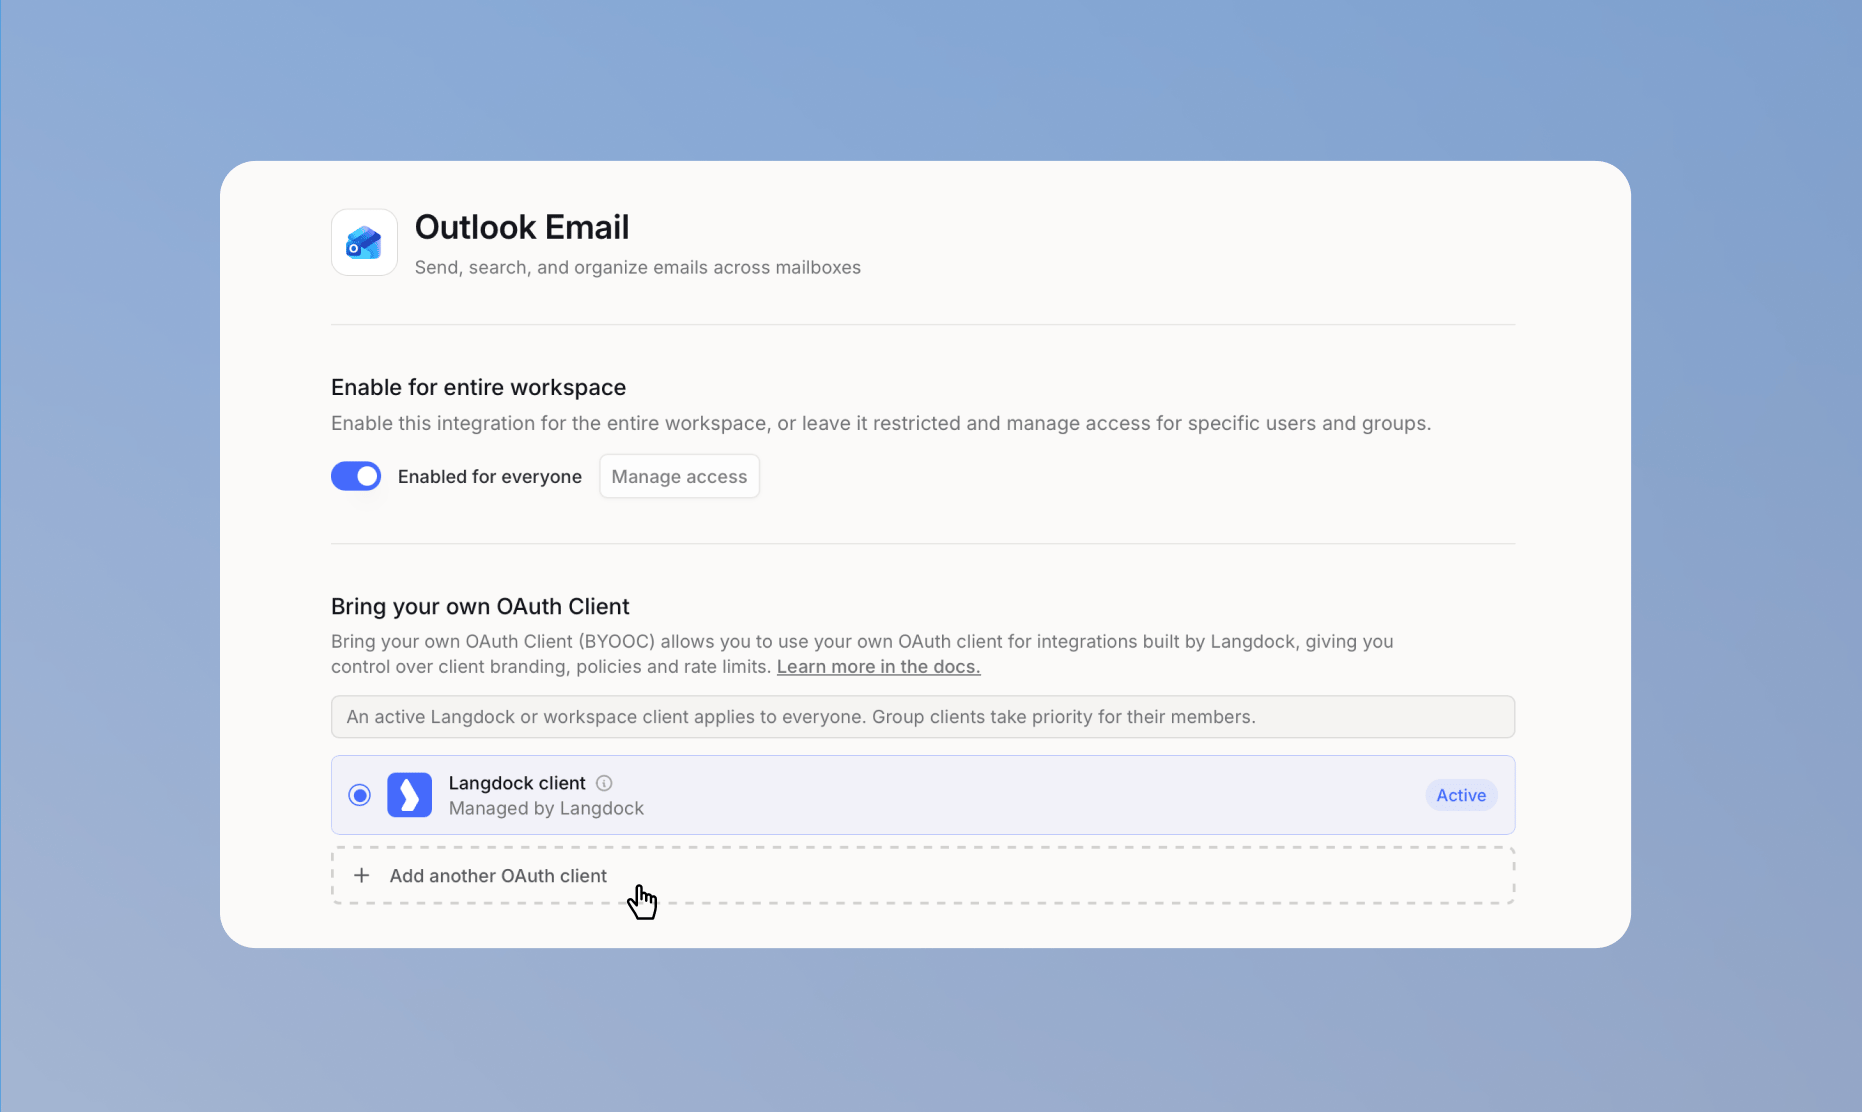
Go to Workspace settings → Integrations, select the integration, and scroll to Bring your own OAuth Client.Click Add another OAuth client when the integration includes a Langdock client. If the integration requires your own client, click Configure your OAuth client to use this integration.In the configuration dialog, copy the Redirect URL into your OAuth app and review the Scopes section. Make sure all listed scopes are enabled in your OAuth app — missing scopes will cause an insufficient scopes error. You can copy all scopes at once using the copy button.For integrations with action-level permissions, we recommend keeping Sync scopes with enabled actions turned on by default. Langdock then requests the auth scopes plus the scopes required by enabled or shared actions, keeping requested scopes aligned with the actions your workspace can use. Learn more in Manage Action-Level Scopes.Optionally add a descriptive Name. Under Access, choose Entire workspace, User choice, or Groups. Enter your Client ID and Client secret (and Tenant ID if prompted for Microsoft integrations). If the integration shows extra connection fields, set those under OAuth connection details, then click Save and confirm the change.
Select the saved client from the client list and confirm the switch to activate it.
Once active, a workspace or group client applies automatically when no User choice client is active. A User choice client is used only when a member selects it. The connection only works if the credentials are valid. Existing connections stay linked to the client they were created with.
Use group access when different parts of your organization need separate OAuth applications for the same integration. For example, assign one client to a subsidiary with its own Microsoft Entra tenant, or use a separate client when a department needs a different approved scope set. When no User choice client is active, the client for your entire workspace remains the default for everyone who is not covered by a group client. When a User choice client is active, members choose among the active User choice clients, the workspace client, and group clients for groups they belong to.
1
Add another custom client
Click Add another OAuth client. Optionally give the client a descriptive name so you can identify it in the client list.
2
Manage client access
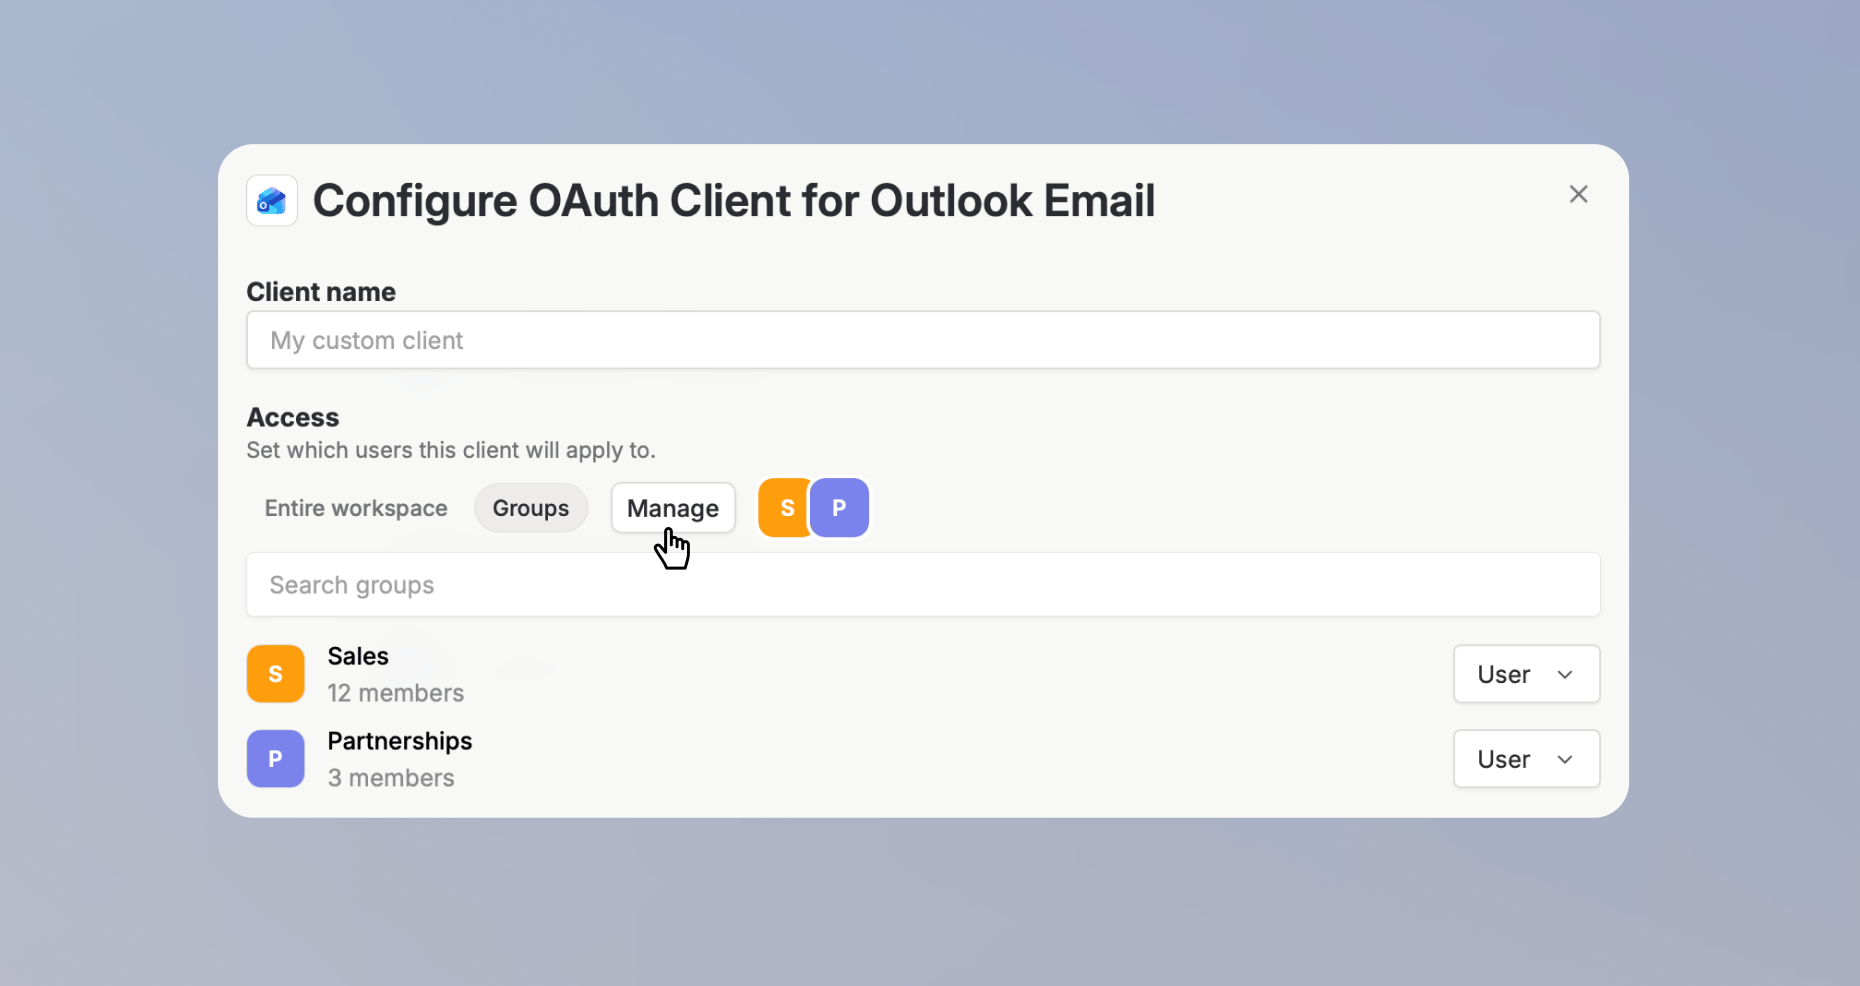
In the Access section, select Groups, then click Manage to choose the user group that should use this client.
3
Add credentials
Enter the Client ID, Client secret, and any fields required by the provider. Click Save and confirm the change. Select the saved client from the client list and confirm the switch to activate it.
Keep a client active for the entire workspace if users without a group client need to connect. A user cannot belong to groups assigned to two active OAuth clients for the same integration.
The redirect URL must match exactly. Any mismatch will cause redirect_uri_mismatch errors. The exact domain depends on your Langdock deployment — always copy the redirect URL from the dialog rather than constructing it manually.
Displays the OAuth scopes required for the integration to function correctly. For example, Jira requires scopes like read:jira-work, write:jira-work, read:jira-user, offline_access, and manage:jira-configuration.
Copy: Copy all scopes to your clipboard for pasting into your OAuth app configuration.
Edit: Switch to edit mode to customize scopes in a text area (advanced use cases only).
Reset to default scopes: Restore the original scope list if you have modified it.
For integrations with action-level permissions, keep Sync scopes with enabled actions turned on unless you intentionally want to manage a fixed scope list yourself. This is the recommended default because Langdock can keep OAuth scopes in sync with enabled and shared actions.
All listed scopes must be enabled in your OAuth app. Missing scopes will cause insufficient_scope errors when users try to connect.
Enter your OAuth application credentials:
Name (optional): A descriptive name that identifies the client in Langdock
Client ID (required): Your app’s public identifier
Client secret (required for most integrations): Your app’s private key, stored encrypted
Tenant ID (Microsoft integrations only, optional): Your Azure AD tenant identifier
OAuth connection details (when shown): extra fields for that client, each marked Optional
Some integrations ask for extra connection fields, such as an instance URL, subdomain, or store domain. Save those values as a workspace default so members skip that prompt when they connect.
On the Langdock client card, click Configure when those fields appear. On dedicated deployments, that card is labeled Global client.
On a custom client, the same fields appear in the configuration dialog and apply only to that client. A Langdock-client default does not apply to a custom-client connection.
Leave a field empty if members should type it when they connect. Enter a value to set the default, for example https://acme.service-now.com. Each field is marked Optional.
If every extra field already has a saved value, members go straight to sign-in. If any field is empty, they still enter it. Workspace admins who see that dialog get a banner with a link back to the integration settings page.
Microsoft Tenant ID stays a separate field in the credentials dialog. Existing connections keep their stored values. New connections and reauthorization use the current defaults.
Each card shows the client name, access type, scope mode, and active status.
Select an inactive client card to activate it.
Select an active custom client card to deactivate it.
Click the settings icon to edit the client.
Open the client settings and click Delete OAuth client credentials to remove it.
Select Langdock client to use the managed client for new connections. This deactivates all custom clients.
You can keep several User choice clients active at the same time as one workspace client and group clients whose members do not overlap. Only one client for the entire workspace can be active for an integration.
Deactivating a client stops new connections from using it. Existing connections remain linked to their selected client. If you delete a client, existing access tokens can keep working until authentication fails. Reauthorization keeps a connection on its client while that client still exists. If the client is gone and User choice is active, reauthorization does not offer a new client, so the member creates a new connection. If no User choice client is active, reauthorization uses the same automatic group or workspace client as a new connection.
You can add a custom Miro OAuth client for branding, tenant policies, or rate limits. If the Miro integration settings show OAuth client required, your deployment has no managed client yet, and users cannot connect until you add one.
Show how to configure a Miro OAuth client
Miro returns the refresh token Langdock needs for automatic token refresh only when Expire user authorization token is enabled. You cannot change this setting after the app is created. If you already created the app without it, creating a connection fails with a Refresh token not found error. Create a new Miro app with the option enabled and replace the Client ID and Client secret in Langdock.
1
Create the app in Miro
You need a Developer team in Miro to create apps. Sign in to Miro, click your avatar, and select Settings. Open the Your apps tab and click + Create new app.Enter an app name, select your Developer team, and select the Expire user authorization token checkbox. Click Create app.
2
Connect the app with Langdock
Add the Redirect URL from Langdock’s Miro integration settings as a redirect URI in your Miro app, then enable every permission listed under Scopes in the Miro app. Miro applies the permissions configured in the app rather than requesting them during authorization.Enter the Client ID and Client secret from your Miro app in Langdock as described in How Custom OAuth Works.
Some of our integrations can only be used when providing your own OAuth client. Details on how to connect them with Langdock are described in this section.
UiPath has no Langdock-managed OAuth client. External applications are registered per Automation Cloud organization, so a UiPath admin must create a confidential application in your organization before users can connect Orchestrator.
Show how to configure a UiPath OAuth client
In UiPath
Open organization Admin → External applications → OAuth apps.
Click Add application and choose Confidential application.
Under Orchestrator, grant the scopes shown in Langdock on User Scope(s) only. Leave Application Scope(s) empty.
Click Configure your OAuth client to use this integration.
Paste the Application ID and app secret, save, and activate the client.
Required authentication fields
UiPath Cloud URL (organization and tenant)
Save UiPath Cloud URL as a workspace default in OAuth connection details, for example https://cloud.uipath.com/acme/DefaultTenant/orchestrator_/. If you leave it empty, the connecting member pastes a URL like that, or enters org / org/tenant. Langdock runs a user-delegated OAuth flow with that user’s Orchestrator permissions.Full guides
Are self-hosted or cloud-hosted accounts supported?
Only UiPath Automation Cloud. Automation Suite and other self-hosted hosts are not supported.
Why is there no Langdock-managed OAuth client?
External OAuth apps are registered per UiPath organization. A client from one organization cannot cover every Langdock customer, so each organization creates its own confidential application.
Are any special account permissions / roles required?
Yes.
A UiPath admin creates the external application.
Scopes go under User Scope(s) for Orchestrator, not Application Scope(s).
Connecting users need Orchestrator access to the folders and processes they use in Langdock.
What about UiPath Automation Hub?
Separate integration. It uses an Open API token (API key), not this OAuth client.See the UiPath setup guide for token setup and least-privilege guidance.
To enable this integration for your workspace, your ServiceNow system administrator must create an OAuth client, in the form of an application registry in ServiceNow, following this documentation. Required authentication fields
Provide ServiceNow Subdomain
Save the ServiceNow subdomain as a workspace default in OAuth connection details. If you leave it empty, members enter it when they connect.
Are self-hosted or cloud-hosted accounts supported?
Only Cloud-hosted accounts are currently supported.
Is a paid ServiceNow plan required?
A paid ServiceNow account is required to create an application registry. View ServiceNow’s plans here.
Are any special account permissions / roles required?
Yes. To connect by OAuth, your systems administrator should set up the right configuration within your instance to connect any user using an OAuth connection. E.g. all users need the oauth_user role to be able to connect. Learn more about ServiceNow’s groups and permissions
Are there usage limits?
Yes. ServiceNow implements rate limiting to prevent excessive API usage. System administrators can configure rules that restrict the number of inbound REST API requests processed per hour. Learn more about ServiceNow’s usage limits.
Shopify Admin has no Langdock managed OAuth app. A workspace admin creates an app in the Shopify Dev Dashboard and pastes the Client ID and Client Secret into Langdock. Connections use application-level permissions: Langdock acts with the app’s Admin API scopes, not the personal Shopify role of the person who installed it.
Show how to configure a Shopify Admin OAuth client
Store domain (a custom domain, a *.myshopify.com domain, or the store handle)
Save the store domain as a workspace default in OAuth connection details, for example acme-store.myshopify.com. If you leave it empty, members enter it when they connect.Copy from Langdock into the Shopify app
Redirect URL from the Shopify Admin OAuth client dialog
Admin API scopes shown in that dialog (or the full list in the setup guide)
Configuring your own OAuth client for Snowflake gives you control over authentication policies, token validity periods, and IP allowlisting within your Snowflake environment.
Show how to configure a Snowflake OAuth client
Required Information:
OAuth Redirect URL: Copy this from Langdock’s Snowflake integration settings page
Client ID: Generated by Snowflake after creating the security integration
Client Secret: Generated by Snowflake after creating the security integration
Authorization URL: Your Snowflake account’s authorization endpoint
The Redirect URL from Langdock must be provided in Snowflake, while the Client ID, Client Secret, and Authorization URL from Snowflake must be entered into Langdock’s integration settings.
If your Snowflake account has network policies or IP allowlisting enabled, you may need to whitelist Langdock’s static IP address to allow connections. See Static IP Configuration for details.
Replace <integration_name> with a descriptive name and <your_redirect_uri> with the OAuth Redirect URL from Step 1.
Run the query to create your new security integration in Snowflake.
Note: Adjust your OAUTH_REFRESH_TOKEN_VALIDITY value based on your security policies.
3
Retrieve Client ID and Client Secret
Show how to retrieve your Client ID, and Secret from Snowflake
Within the same workspace, run the following query:
Snowflake OAuth uses roles rather than scopes. Leave Scopes empty so each connecting user gets their default Snowflake role. If you enter a session role such as session:role:SYSADMIN, every user authenticates against that role. Users who do not have it in Snowflake cannot connect.
6
Test the Connection
Show how to add a Connection to your Snowflake Integration
Click “Add Connection” in your Snowflake integration.
You should be directed to the Snowflake Authorization screen
Log into your Snowflake account
You have now successfully set up your own OAuth Snowflake integration!
Was this page helpful?
{"docsConfig":{"theme":"mint","$schema":"https://mintlify.com/docs.json","name":"Docs","colors":{"primary":"#4469FC","light":"#ECF0FF","dark":"#0D001D"},"logo":{"light":"https://mintcdn.com/langdock-34/URgvNwU7CYGZq8R7/logo/light.svg?fit=max\u0026auto=format\u0026n=URgvNwU7CYGZq8R7\u0026q=85\u0026s=594b4bd597e2629fb1a7dccfae6aa1c4","dark":"https://mintcdn.com/langdock-34/URgvNwU7CYGZq8R7/logo/dark.svg?fit=max\u0026auto=format\u0026n=URgvNwU7CYGZq8R7\u0026q=85\u0026s=d063d52fb4d331afb82adad972214673"},"favicon":"https://mintcdn.com/langdock-34/KbxhVmfYOcTup72x/favicon.png?fit=max\u0026auto=format\u0026n=KbxhVmfYOcTup72x\u0026q=85\u0026s=e12cd6cccfe5c94bf4ae6ea4fba7959c","background":{"color":{"dark":"#090014"}},"navbar":{"primary":{"type":"button","label":"Back to app","href":"https://app.langdock.com"}},"footer":{"socials":{"linkedin":"https://www.linkedin.com/company/langdock"}},"errors":{"404":{"redirect":true}},"contextual":{"options":["copy","view","mcp","cursor","vscode",{"title":"Ask Langdock","description":"Ask Langdock about the current page","icon":"/favicon.png","href":{"base":"https://app.langdock.com/chat","query":[{"key":"q","value":"Read from https://docs.langdock.com$path.md so I can ask questions about it."},{"key":"sendPrompt","value":"true"}]}}],"display":"header"},"styling":{"latex":true},"navigation":{"global":{"anchors":[{"anchor":"Changelog","icon":"newspaper","href":"https://www.langdock.com/changelog"},{"anchor":"Status","icon":"signal-bars","href":"https://status.langdock.com/"},{"anchor":"Support","icon":"messages-question","href":"https://www.langdock.com/contact-us"}]},"languages":[{"language":"en","default":true,"href":"en/using-langdock/get-started/introduction"},{"language":"de","href":"de/using-langdock/get-started/introduction"}]}},"deployment":{"deploymentMetadataValue":{"subdomain":"langdock-34","hasAudioNarration":false,"actualSubdomain":"langdock-34","customDomains":["docs.langdock.com"],"gitSource":{"type":"github","owner":"langdock","repo":"docs","deployBranch":"main","contentDirectory":"","isPrivate":true,"mountPath":"","label":""},"feedback":{"thumbs":true,"agentFeedback":false},"entitlements":{"AI_CHAT":{"status":"ENABLED"},"REMOVE_BRANDING":{"status":"DISABLED"},"CONTEXTUAL_FEEDBACK":{"status":"DISABLED"},"CODE_SNIPPET_FEEDBACK":{"status":"DISABLED"},"WEB_MCP":{"status":"ENABLED"},"NARRATION":{"status":"ENABLED"}},"buildId":"6af43e9ff70ad676a5c54f19","clientVersion":"0.0.4102","searchFilterCounts":[{"language":"en","tag":"Using Langdock","count":152},{"language":"de","tag":"Langdock nutzen","count":152},{"language":"en","tag":"Developer","count":141},{"language":"de","tag":"Entwickler","count":141},{"language":"en","tag":"Admin","count":111},{"language":"de","tag":"Admin","count":111},{"language":"en","tag":"Manage Integrations","count":43},{"language":"de","tag":"Integrationen verwalten","count":43},{"language":"en","tag":"Guides","count":40},{"language":"de","tag":"Anleitungen","count":40},{"language":"en","tag":"Billing API","count":36},{"language":"de","tag":"Billing API","count":36},{"language":"en","tag":"Workflows","count":28},{"language":"de","tag":"Workflows","count":28},{"language":"en","tag":"Integrations","count":19},{"language":"de","tag":"Integrationen","count":19},{"language":"en","tag":"Node Types","count":18},{"language":"de","tag":"Node Types","count":18},{"language":"en","tag":"Integration Setup Guides","count":17},{"language":"de","tag":"Integrations-Setup-Anleitungen","count":17}]},"assistantConfig":{"deflection":{"enabled":false}},"basePath":"","hasChatPermissions":true,"hasWebMcpPermissions":true,"toggles":[{"name":"kill-isr","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-rbac-roles","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-mintlify-slack","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"agent-integrations-settings","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"rbac-expansion","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-pr-grouping","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"custom-prefix","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"analytics-v7","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"user-flows-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"no-publish-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-onboarding","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"llms-txt-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving-live","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"stripTemperatureMiddleware","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"support-platform-pylon-zendesk","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"snapshot-serving","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"instant-rollback","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications-server","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"granular-notifications","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automations-fable","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fixed-ai-action-pricing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"automation-resolve-merge-conflict","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"scoped-publishing","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"mintql","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"page-level-analytics","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-version-history-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"billing-page-v2","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"full-page-search","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workspace-projects","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"assistant-v5","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"fork-pr-previews","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"revalidation-jwt","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-sso-scim","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"hobby-abuse-scan","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"dashboard-inbox","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-signup","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-dual-write","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"workos-enabled","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"approve-review-flow","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"editor-metadata","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"sso-setup-deadline-banner","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"turbopuffer-serve","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false},{"name":"live-agents","enabled":true,"variant":{"name":"disabled","enabled":false,"feature_enabled":true},"impressionData":false}],"googleFontsInlined":false},"customCss":[],"page":{"pagePath":"en/admin/manage-integrations/bring-your-own-oauth","slug":"/en/admin/manage-integrations/bring-your-own-oauth","pageMetadata":{"title":"Bring Your Own OAuth Client","sidebarTitle":"Bring Your Own OAuth Client","description":"Set up custom OAuth applications for integrations, assign clients to your workspace or user groups, and control scopes, tenant policies, and branding.","keywords":["oauth","authentication","integrations","custom client","user groups","security","branding"],"href":"/en/admin/manage-integrations/bring-your-own-oauth"},"description":{"compiledSource":"\"use strict\";\nconst {jsx: _jsx} = arguments[0];\nconst {useMDXComponents: _provideComponents} = arguments[0];\nfunction _createMdxContent(props) {\n const _components = {\n p: \"p\",\n ..._provideComponents(),\n ...props.components\n };\n return _jsx(_components.p, {\n children: \"Set up custom OAuth applications for integrations, assign clients to your workspace or user groups, and control scopes, tenant policies, and branding.\"\n });\n}\nfunction MDXContent(props = {}) {\n const {wrapper: MDXLayout} = {\n ..._provideComponents(),\n ...props.components\n };\n return MDXLayout ? _jsx(MDXLayout, {\n ...props,\n children: _jsx(_createMdxContent, {\n ...props\n })\n }) : _createMdxContent(props);\n}\nreturn {\n default: MDXContent\n};\n","frontmatter":{},"scope":{}},"pageType":"default","mdx":{"mdxSource":{"compiledSource":"\"use strict\";const{Fragment:_Fragment,jsx:_jsx,jsxs:_jsxs}=arguments[0];const{useMDXComponents:_provideComponents}=arguments[0];function _createMdxContent(props){const _components={a:`a`,br:`br`,code:`code`,hr:`hr`,li:`li`,ol:`ol`,p:`p`,pre:`pre`,span:`span`,strong:`strong`,ul:`ul`,..._provideComponents(),...props.components},{Accordion,AccordionGroup,CodeBlock,Expandable,Frame,Heading,Info,Note,OptimizedImage,Step,Steps,Tab,Tabs,Warning}=_components;if(!Accordion)_missingMdxReference(`Accordion`,true);if(!AccordionGroup)_missingMdxReference(`AccordionGroup`,true);if(!CodeBlock)_missingMdxReference(`CodeBlock`,true);if(!Expandable)_missingMdxReference(`Expandable`,true);if(!Frame)_missingMdxReference(`Frame`,true);if(!Heading)_missingMdxReference(`Heading`,true);if(!Info)_missingMdxReference(`Info`,true);if(!Note)_missingMdxReference(`Note`,true);if(!OptimizedImage)_missingMdxReference(`OptimizedImage`,true);if(!Step)_missingMdxReference(`Step`,true);if(!Steps)_missingMdxReference(`Steps`,true);if(!Tab)_missingMdxReference(`Tab`,true);if(!Tabs)_missingMdxReference(`Tabs`,true);if(!Warning)_missingMdxReference(`Warning`,true);return _jsxs(_Fragment,{children:[_jsx(Info,{children:_jsxs(_components.p,{children:[`You can use multiple custom OAuth clients for the same integration. Set one client for your entire workspace, offer `,_jsx(_components.strong,{children:`User choice`}),` clients that members pick before they connect, or assign clients to specific user groups.`]})}),`\n`,_jsx(Heading,{level:`2`,id:`how-custom-oauth-works`,children:`How Custom OAuth Works`}),`\n`,_jsxs(_components.p,{children:[`When you configure a custom OAuth client, Langdock routes new authentication flows through your OAuth application instead of the default Langdock client. A workspace client applies by default, and a group client applies to members of its groups. `,_jsx(_components.strong,{children:`User choice`}),` is available for OAuth integrations, including built-in integrations. It is not available for MCP servers, OAuth 2.0 (Dynamic Client Registration), or OAuth 2.0 (CIMD). When any `,_jsx(_components.strong,{children:`User choice`}),` client is active, members choose a client before they connect, and that choice takes priority over the workspace client and group clients. This means:`]}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Your branding`}),` (custom name and logo) appears in consent screens`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Your tenant policies`}),` control user access and admin consent requirements`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Your rate limits`}),` apply to API calls made by your users`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Your user groups`}),` can authenticate through separate OAuth clients`]}),`\n`]}),`\n`,_jsxs(Steps,{children:[_jsxs(Step,{title:`Create OAuth App at Provider`,children:[_jsx(_components.p,{children:`Register a new OAuth application in your provider’s developer portal (Google Cloud Console, Microsoft Azure, etc.).`}),_jsx(_components.p,{children:_jsx(_components.strong,{children:`Required Configuration:`})}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Copy the exact redirect URL from Langdock’s integration settings`}),`\n`,_jsx(_components.li,{children:`Select all required scopes shown in Langdock for that integration`}),`\n`,_jsx(_components.li,{children:`Configure any tenant-specific settings (admin consent, allowlisting)`}),`\n`]})]}),_jsxs(Step,{title:`Gather Credentials`,children:[_jsx(_components.p,{children:`Note down the following from your OAuth app:`}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Client ID`}),` (always required)`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Client secret`}),` (required for most integrations)`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Tenant ID`}),` (optional, shown for Microsoft integrations only)`]}),`\n`]})]}),_jsxs(Step,{title:`Configure in Langdock`,children:[_jsxs(_components.p,{children:[`Go to `,_jsx(_components.a,{href:`https://app.langdock.com/settings/workspace/products/integrations`,children:_jsx(_components.strong,{children:`Workspace settings → Integrations`})}),`, select the integration, and scroll to `,_jsx(_components.strong,{children:`Bring your own OAuth Client`}),`.`]}),_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Add another OAuth client`}),` when the integration includes a Langdock client. If the integration requires your own client, click `,_jsx(_components.strong,{children:`Configure your OAuth client to use this integration.`})]}),_jsxs(_components.p,{children:[`In the configuration dialog, copy the `,_jsx(_components.strong,{children:`Redirect URL`}),` into your OAuth app and review the `,_jsx(_components.strong,{children:`Scopes`}),` section. Make sure all listed scopes are enabled in your OAuth app — missing scopes will cause an insufficient scopes error. You can copy all scopes at once using the copy button.`]}),_jsxs(_components.p,{children:[`For integrations with action-level permissions, we recommend keeping `,_jsx(_components.strong,{children:`Sync scopes with enabled actions`}),` turned on by default. Langdock then requests the auth scopes plus the scopes required by enabled or shared actions, keeping requested scopes aligned with the actions your workspace can use. Learn more in `,_jsx(_components.a,{href:`/en/admin/manage-integrations/manage-action-level-scopes`,children:`Manage Action-Level Scopes`}),`.`]}),_jsxs(_components.p,{children:[`Optionally add a descriptive `,_jsx(_components.strong,{children:`Name`}),`. Under `,_jsx(_components.strong,{children:`Access`}),`, choose `,_jsx(_components.strong,{children:`Entire workspace`}),`, `,_jsx(_components.strong,{children:`User choice`}),`, or `,_jsx(_components.strong,{children:`Groups`}),`. Enter your `,_jsx(_components.strong,{children:`Client ID`}),` and `,_jsx(_components.strong,{children:`Client secret`}),` (and `,_jsx(_components.strong,{children:`Tenant ID`}),` if prompted for Microsoft integrations). If the integration shows extra connection fields, set those under `,_jsx(_components.strong,{children:`OAuth connection details`}),`, then click `,_jsx(_components.strong,{children:`Save`}),` and confirm the change.`]}),_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_access.png?fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=1b9b5f1cb9c5c3d6ac45e3aed1cb3667`,alt:`OAuth client dialog with Access set to Entire workspace, and User choice and Groups beside it`,style:{borderRadius:`6px`},\"data-og-width\":`1840`,width:`1840`,\"data-og-height\":`1850`,height:`1850`,\"data-path\":`images/oauth_user_choice_access.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_access.png?w=280\u0026fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=699911d1e58bc61e7fd078a2996de0fe 280w, https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_access.png?w=560\u0026fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=e617caa3e94d24360d9c97c1a4d436af 560w, https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_access.png?w=840\u0026fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=65311739a9beee8394c7565c5d19e02d 840w, https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_access.png?w=1100\u0026fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=039ffa82e130d0c956e7967f6b6875da 1100w, https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_access.png?w=1650\u0026fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=10bc65c0b1edfc0f26f88c2e1d80b6a7 1650w, https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_access.png?w=2500\u0026fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=85fddf227e13499a573755f1e0f5f704 2500w`})}),_jsx(_components.p,{children:`Select the saved client from the client list and confirm the switch to activate it.`}),_jsx(Warning,{children:_jsxs(_components.p,{children:[`Once active, a workspace or group client applies automatically when no `,_jsx(_components.strong,{children:`User choice`}),` client is active. A `,_jsx(_components.strong,{children:`User choice`}),` client is used only when a member selects it. The connection only works if the credentials are valid. Existing connections stay linked to the client they were created with.`]})})]}),_jsxs(Step,{title:`Test Authentication`,children:[_jsx(_components.p,{children:`Have a user connect their account to verify:`}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Consent screen shows your client`}),`\n`,_jsx(_components.li,{children:`Required scopes are granted`}),`\n`,_jsx(_components.li,{children:`Data access works as expected through actions`}),`\n`]})]})]}),`\n`,_jsx(Heading,{level:`2`,id:`assign-oauth-clients-to-user-groups`,children:`Assign OAuth Clients to User Groups`}),`\n`,_jsxs(_components.p,{children:[`Use group access when different parts of your organization need separate OAuth applications for the same integration. For example, assign one client to a subsidiary with its own Microsoft Entra tenant, or use a separate client when a department needs a different approved scope set. When no `,_jsx(_components.strong,{children:`User choice`}),` client is active, the client for your entire workspace remains the default for everyone who is not covered by a group client. When a `,_jsx(_components.strong,{children:`User choice`}),` client is active, members choose among the active `,_jsx(_components.strong,{children:`User choice`}),` clients, the workspace client, and group clients for groups they belong to.`]}),`\n`,_jsxs(Steps,{children:[_jsxs(Step,{title:`Add another custom client`,children:[_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients1.png?fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=faee51ddc0a784bd2a001c4c085e7eca`,alt:`Outlook Email integration settings with Add another OAuth client selected`,style:{borderRadius:`6px`},\"data-og-width\":`1862`,width:`1862`,\"data-og-height\":`1112`,height:`1112`,\"data-path\":`images/multiple_oauth_clients1.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients1.png?w=280\u0026fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=93b6d00b7217b0e3237c950af2ebaf70 280w, https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients1.png?w=560\u0026fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=1df4eb946c69939addc403181e6329b8 560w, https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients1.png?w=840\u0026fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=ee4f5eca365d0966ffb23084b7df2b66 840w, https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients1.png?w=1100\u0026fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=c9a4e173c116946b439cb23d618f4c82 1100w, https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients1.png?w=1650\u0026fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=847fa3021886a5ea993fb494a9de26fc 1650w, https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients1.png?w=2500\u0026fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=bb6a1edadefdaaf9e964003108321730 2500w`})}),_jsxs(_components.p,{children:[`Click `,_jsx(_components.strong,{children:`Add another OAuth client`}),`. Optionally give the client a descriptive name so you can identify it in the client list.`]})]}),_jsxs(Step,{title:`Manage client access`,children:[_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients2.png?fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=0cbc08bc7ed94034021d321fe159126c`,alt:`OAuth client access settings with user groups selected`,style:{borderRadius:`6px`},\"data-og-width\":`1860`,width:`1860`,\"data-og-height\":`986`,height:`986`,\"data-path\":`images/multiple_oauth_clients2.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients2.png?w=280\u0026fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=856e39a6d029186a80dfa27a5b183ac3 280w, https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients2.png?w=560\u0026fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=9240470a40738ddb11e4d7517aa3a80a 560w, https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients2.png?w=840\u0026fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=b5ce854d1721b9b7fb4c91858e051382 840w, https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients2.png?w=1100\u0026fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=947479929fd6671253e0f3c0d058362f 1100w, https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients2.png?w=1650\u0026fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=09d79416cc28abec7aaa42178ef5241f 1650w, https://mintcdn.com/langdock-34/yXe3zblEcJbCwgSJ/images/multiple_oauth_clients2.png?w=2500\u0026fit=max\u0026auto=format\u0026n=yXe3zblEcJbCwgSJ\u0026q=85\u0026s=f54449797a60f3955a2ae31ad708345c 2500w`})}),_jsxs(_components.p,{children:[`In the `,_jsx(_components.strong,{children:`Access`}),` section, select `,_jsx(_components.strong,{children:`Groups`}),`, then click `,_jsx(_components.strong,{children:`Manage`}),` to choose the user group that should use this client.`]})]}),_jsx(Step,{title:`Add credentials`,children:_jsxs(_components.p,{children:[`Enter the Client ID, Client secret, and any fields required by the provider. Click `,_jsx(_components.strong,{children:`Save`}),` and confirm the change. Select the saved client from the client list and confirm the switch to activate it.`]})})]}),`\n`,_jsx(Warning,{children:_jsx(_components.p,{children:`Keep a client active for the entire workspace if users without a group client need to connect. A user cannot belong to groups assigned to two active OAuth clients for the same integration.`})}),`\n`,_jsx(Heading,{level:`2`,id:`integration-settings-interface`,children:`Integration Settings Interface`}),`\n`,_jsx(_components.p,{children:`The configuration dialog contains the following sections:`}),`\n`,_jsxs(Tabs,{children:[_jsxs(Tab,{title:`Redirect URL`,id:`redirect-url`,children:[_jsx(_components.p,{children:`A read-only field displaying the redirect URL your OAuth app must use. Click the copy button to copy it exactly. The URL format is:`}),_jsx(CodeBlock,{numberOfLines:`2`,language:`text`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`text`,children:_jsxs(_components.code,{language:`text`,numberOfLines:`2`,children:[_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:`https://app.langdock.com/api/integrations/{integration-id}/callback`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{})})]})})}),_jsx(Warning,{children:_jsxs(_components.p,{children:[`The redirect URL must match exactly. Any mismatch will cause `,_jsx(_components.code,{children:`redirect_uri_mismatch`}),` errors. The exact domain depends on your Langdock deployment — always copy the redirect URL from the dialog rather than constructing it manually.`]})})]}),_jsxs(Tab,{title:`Scopes`,id:`scopes`,children:[_jsxs(_components.p,{children:[`Displays the OAuth scopes required for the integration to function correctly. For example, Jira requires scopes like `,_jsx(_components.code,{children:`read:jira-work`}),`, `,_jsx(_components.code,{children:`write:jira-work`}),`, `,_jsx(_components.code,{children:`read:jira-user`}),`, `,_jsx(_components.code,{children:`offline_access`}),`, and `,_jsx(_components.code,{children:`manage:jira-configuration`}),`.`]}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Copy`}),`: Copy all scopes to your clipboard for pasting into your OAuth app configuration.`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Edit`}),`: Switch to edit mode to customize scopes in a text area (advanced use cases only).`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Reset to default scopes`}),`: Restore the original scope list if you have modified it.`]}),`\n`]}),_jsxs(_components.p,{children:[`For integrations with action-level permissions, keep `,_jsx(_components.strong,{children:`Sync scopes with enabled actions`}),` turned on unless you intentionally want to manage a fixed scope list yourself. This is the recommended default because Langdock can keep OAuth scopes in sync with enabled and shared actions.`]}),_jsx(Warning,{children:_jsxs(_components.p,{children:[`All listed scopes must be enabled in your OAuth app. Missing scopes will cause `,_jsx(_components.code,{children:`insufficient_scope`}),` errors when users try to connect.`]})})]}),_jsxs(Tab,{title:`Credentials`,id:`credentials`,children:[_jsx(_components.p,{children:`Enter your OAuth application credentials:`}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Name`}),` (optional): A descriptive name that identifies the client in Langdock`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Client ID`}),` (required): Your app’s public identifier`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Client secret`}),` (required for most integrations): Your app’s private key, stored encrypted`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Tenant ID`}),` (Microsoft integrations only, optional): Your Azure AD tenant identifier`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`OAuth connection details`}),` (when shown): extra fields for that client, each marked `,_jsx(_components.strong,{children:`Optional`})]}),`\n`]})]})]}),`\n`,_jsx(Heading,{level:`2`,id:`additional-parameters`,children:`OAuth connection details`}),`\n`,_jsx(_components.p,{children:`Some integrations ask for extra connection fields, such as an instance URL, subdomain, or store domain. Save those values as a workspace default so members skip that prompt when they connect.`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`On the `,_jsx(_components.strong,{children:`Langdock client`}),` card, click `,_jsx(_components.strong,{children:`Configure`}),` when those fields appear. On dedicated deployments, that card is labeled `,_jsx(_components.strong,{children:`Global client`}),`.`]}),`\n`,_jsx(_components.li,{children:`On a custom client, the same fields appear in the configuration dialog and apply only to that client. A Langdock-client default does not apply to a custom-client connection.`}),`\n`,_jsxs(_components.li,{children:[`Leave a field empty if members should type it when they connect. Enter a value to set the default, for example `,_jsx(_components.code,{children:`https://acme.service-now.com`}),`. Each field is marked `,_jsx(_components.strong,{children:`Optional`}),`.`]}),`\n`]}),`\n`,_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_1.png?fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=f5278954a26e692a3d526bb26ad16781`,alt:`Example ServiceNow integration: Langdock client card with Configure, and Add another OAuth client`,style:{borderRadius:`6px`},\"data-og-width\":`1840`,width:`1840`,\"data-og-height\":`510`,height:`510`,\"data-path\":`images/oauth_connection_details_1.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_1.png?w=280\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=f5fa1a22f209e60b3e60a7ca563fe278 280w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_1.png?w=560\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=ae75b168776bc9e41b4157cedef57db8 560w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_1.png?w=840\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=7d4e235d100cee5f5bbf46aa9e48a9b1 840w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_1.png?w=1100\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=a6a499b7a6453f41c5d8733c9c46e863 1100w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_1.png?w=1650\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=85cb71adbdb38469e3dd7372056cd231 1650w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_1.png?w=2500\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=a0b2bc5c0a7fbe21551e6a463c521b6c 2500w`})}),`\n`,_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_2.png?fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=2d006c74f3f42c18a208f72c18801346`,alt:`Configure dialog with workspace default https://acme.service-now.com in the optional ServiceNow URL or subdomain field`,style:{borderRadius:`6px`},\"data-og-width\":`1840`,width:`1840`,\"data-og-height\":`1112`,height:`1112`,\"data-path\":`images/oauth_connection_details_2.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_2.png?w=280\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=77bca75b3449b69580894b760f55b52d 280w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_2.png?w=560\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=35303c7c2982fca28c71f9cdf74234e6 560w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_2.png?w=840\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=d5c2898d80a40bea9887dfdfa9a79847 840w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_2.png?w=1100\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=1aca34d6103feff4da6e64f551154645 1100w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_2.png?w=1650\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=fef563b99e83745a89f72cf9572ba129 1650w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_2.png?w=2500\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=893804fae6f3409c4cf29f27836d00da 2500w`})}),`\n`,_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_3.png?fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=b97dec944f45d292729063452500b67f`,alt:`Add custom OAuth client dialog for ServiceNow, with the same optional OAuth connection details fields`,style:{borderRadius:`6px`},\"data-og-width\":`1840`,width:`1840`,\"data-og-height\":`1864`,height:`1864`,\"data-path\":`images/oauth_connection_details_3.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_3.png?w=280\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=a836a56ffeff5899ce56364c943b587d 280w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_3.png?w=560\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=4cafbf06de719a36ae3665536198ecf3 560w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_3.png?w=840\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=4287c6ef6cc63249cd15e34dc7a36625 840w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_3.png?w=1100\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=0f99bbb38b2f36162a9dbb900e1de130 1100w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_3.png?w=1650\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=20fe175838b452654613351e7b06f71c 1650w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_3.png?w=2500\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=685ae8e470dd3dcc8deda9349815a0b2 2500w`})}),`\n`,_jsx(_components.p,{children:`If every extra field already has a saved value, members go straight to sign-in. If any field is empty, they still enter it. Workspace admins who see that dialog get a banner with a link back to the integration settings page.`}),`\n`,_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_4.png?fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=592da4517e7b099d4307f8a6175726db`,alt:`Example ServiceNow connection dialog with an empty extra field and an admin banner linking back to settings`,style:{borderRadius:`6px`},\"data-og-width\":`1840`,width:`1840`,\"data-og-height\":`1084`,height:`1084`,\"data-path\":`images/oauth_connection_details_4.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_4.png?w=280\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=b61d0d45a768adc6bf388d56c8cce3a7 280w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_4.png?w=560\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=7ef480ad222a6225eda9de1a90fae477 560w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_4.png?w=840\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=1b4fe6702e5eff00f3c645208d5ba0a8 840w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_4.png?w=1100\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=49db535f97f477dd2ec23236d5628cb8 1100w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_4.png?w=1650\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=a0fbcc7b9ae52fc49ca59ca22dff75ed 1650w, https://mintcdn.com/langdock-34/KsBXt70lg_eJcgg4/images/oauth_connection_details_4.png?w=2500\u0026fit=max\u0026auto=format\u0026n=KsBXt70lg_eJcgg4\u0026q=85\u0026s=52df5d7f1d789584cf3861269d9690a8 2500w`})}),`\n`,_jsxs(_components.p,{children:[`Microsoft `,_jsx(_components.strong,{children:`Tenant ID`}),` stays a separate field in the credentials dialog. Existing connections keep their stored values. New connections and reauthorization use the current defaults.`]}),`\n`,_jsx(Heading,{level:`2`,id:`manage-custom-oauth-clients`,children:`Manage Custom OAuth Clients`}),`\n`,_jsx(_components.p,{children:`Each card shows the client name, access type, scope mode, and active status.`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Select an inactive client card to activate it.`}),`\n`,_jsx(_components.li,{children:`Select an active custom client card to deactivate it.`}),`\n`,_jsx(_components.li,{children:`Click the settings icon to edit the client.`}),`\n`,_jsxs(_components.li,{children:[`Open the client settings and click `,_jsx(_components.strong,{children:`Delete OAuth client credentials`}),` to remove it.`]}),`\n`,_jsxs(_components.li,{children:[`Select `,_jsx(_components.strong,{children:`Langdock client`}),` to use the managed client for new connections. This deactivates all custom clients.`]}),`\n`]}),`\n`,_jsxs(_components.p,{children:[`You can keep several `,_jsx(_components.strong,{children:`User choice`}),` clients active at the same time as one workspace client and group clients whose members do not overlap. Only one client for the entire workspace can be active for an integration.`]}),`\n`,_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_clients.png?fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=b66fc117d1a461cceccdb88247eb7c61`,alt:`Active OAuth clients Acme Finance and Acme HR, each with the User choice icon`,style:{borderRadius:`6px`},\"data-og-width\":`1840`,width:`1840`,\"data-og-height\":`610`,height:`610`,\"data-path\":`images/oauth_user_choice_clients.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_clients.png?w=280\u0026fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=571de98f39b3869753846fca670570eb 280w, https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_clients.png?w=560\u0026fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=ce1eb5e118b64c7a2ba01c8c4aac5d2e 560w, https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_clients.png?w=840\u0026fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=2b42d7ac568113b09c02cf7ca130bea1 840w, https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_clients.png?w=1100\u0026fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=58f8d00770e92d84dc7f67b65fbdc88c 1100w, https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_clients.png?w=1650\u0026fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=c8e35dadb35584cb11b05c3299b12cb3 1650w, https://mintcdn.com/langdock-34/F_0krru1WSricJHA/images/oauth_user_choice_clients.png?w=2500\u0026fit=max\u0026auto=format\u0026n=F_0krru1WSricJHA\u0026q=85\u0026s=00cfefdf988582b71035dfa40e280002 2500w`})}),`\n`,_jsx(Warning,{children:_jsxs(_components.p,{children:[`Deactivating a client stops new connections from using it. Existing connections remain linked to their selected client. If you delete a client, existing access tokens can keep working until authentication fails. Reauthorization keeps a connection on its client while that client still exists. If the client is gone and `,_jsx(_components.strong,{children:`User choice`}),` is active, reauthorization does not offer a new client, so the member creates a new connection. If no `,_jsx(_components.strong,{children:`User choice`}),` client is active, reauthorization uses the same automatic group or workspace client as a new connection.`]})}),`\n`,_jsx(Heading,{level:`2`,id:`common-configuration-errors`,children:`Common Configuration Errors`}),`\n`,_jsxs(AccordionGroup,{children:[_jsxs(Accordion,{title:`redirect_uri_mismatch`,id:`redirect-uri-mismatch`,children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Cause`}),`: Redirect URL doesn’t match exactly between Langdock and your OAuth app`]}),_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Solution`}),`:`]}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Copy the redirect URL from Langdock exactly`}),`\n`,_jsx(_components.li,{children:`Check for trailing slashes or protocol mismatches`}),`\n`,_jsx(_components.li,{children:`Verify you’re configuring the correct environment`}),`\n`]})]}),_jsxs(Accordion,{title:`invalid_client`,id:`invalid-client`,children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Cause`}),`: Client ID or Client secret is incorrect`]}),_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Solution`}),`:`]}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Double-check credentials from your OAuth app`}),`\n`,_jsx(_components.li,{children:`Ensure no extra spaces or characters`}),`\n`,_jsx(_components.li,{children:`Verify the client is enabled in your provider’s console`}),`\n`]})]}),_jsxs(Accordion,{title:`consent_required`,id:`consent-required`,children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Cause`}),`: Admin consent required but not granted`]}),_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Solution`}),`:`]}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Grant admin consent in your tenant settings`}),`\n`,_jsx(_components.li,{children:`Enable user consent if appropriate for your organization`}),`\n`,_jsx(_components.li,{children:`Check tenant allowlisting requirements`}),`\n`]})]}),_jsxs(Accordion,{title:`insufficient_scope`,id:`insufficient-scope`,children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Cause`}),`: Missing required scopes in your OAuth app`]}),_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Solution`}),`:`]}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Add all scopes shown in Langdock to your OAuth app`}),`\n`,_jsx(_components.li,{children:`Users may need to reconnect after adding scopes`}),`\n`,_jsx(_components.li,{children:`Verify scope names match exactly (case-sensitive)`}),`\n`]})]}),_jsxs(Accordion,{title:`A group client cannot be activated`,id:`a-group-client-cannot-be-activated`,children:[_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Cause`}),`: At least one user belongs to a group covered by another active OAuth client.`]}),_jsxs(_components.p,{children:[_jsx(_components.strong,{children:`Solution`}),`:`]}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Review the groups assigned to both clients`}),`\n`,_jsx(_components.li,{children:`Remove the overlapping group assignment or membership`}),`\n`,_jsx(_components.li,{children:`Activate the client again`}),`\n`]})]})]}),`\n`,_jsx(_components.hr,{}),`\n`,_jsx(Heading,{level:`2`,id:`custom-miro-oauth-client`,children:`Custom Miro OAuth Client`}),`\n`,_jsxs(_components.p,{children:[`You can add a custom Miro OAuth client for branding, tenant policies, or rate limits. If the Miro integration settings show `,_jsx(_components.strong,{children:`OAuth client required`}),`, your deployment has no managed client yet, and users cannot connect until you add one.`]}),`\n`,_jsxs(Expandable,{title:`how to configure a Miro OAuth client`,collapsible:true,children:[_jsx(Warning,{children:_jsxs(_components.p,{children:[`Miro returns the refresh token Langdock needs for automatic token refresh only when `,_jsx(_components.strong,{children:`Expire user authorization token`}),` is enabled. You cannot change this setting after the app is created. If you already created the app without it, creating a connection fails with a `,_jsx(_components.strong,{children:`Refresh token not found`}),` error. Create a new Miro app with the option enabled and replace the `,_jsx(_components.strong,{children:`Client ID`}),` and `,_jsx(_components.strong,{children:`Client secret`}),` in Langdock.`]})}),_jsxs(Steps,{children:[_jsxs(Step,{title:`Create the app in Miro`,children:[_jsxs(_components.p,{children:[`You need a `,_jsx(_components.a,{href:`https://developers.miro.com/docs/create-a-developer-team`,children:`Developer team`}),` in Miro to create apps. Sign in to Miro, click your avatar, and select `,_jsx(_components.strong,{children:`Settings`}),`. Open the `,_jsx(_components.strong,{children:`Your apps`}),` tab and click `,_jsx(_components.strong,{children:`+ Create new app`}),`.`]}),_jsxs(_components.p,{children:[`Enter an app name, select your Developer team, and select the `,_jsx(_components.strong,{children:`Expire user authorization token`}),` checkbox. Click `,_jsx(_components.strong,{children:`Create app`}),`.`]}),_jsx(Frame,{children:_jsx(OptimizedImage,{src:`https://mintcdn.com/langdock-34/oaofNJPqDWePET7M/images/miro_custom_oauth_client.png?fit=max\u0026auto=format\u0026n=oaofNJPqDWePET7M\u0026q=85\u0026s=f654be6983f7a46e078cfc6c7998f64c`,alt:`Miro Create new app dialog with the Expire user authorization token checkbox selected`,style:{borderRadius:`6px`},\"data-og-width\":`1840`,width:`1840`,\"data-og-height\":`1888`,height:`1888`,\"data-path\":`images/miro_custom_oauth_client.png`,\"data-optimize\":`true`,\"data-opv\":`3`,srcset:`https://mintcdn.com/langdock-34/oaofNJPqDWePET7M/images/miro_custom_oauth_client.png?w=280\u0026fit=max\u0026auto=format\u0026n=oaofNJPqDWePET7M\u0026q=85\u0026s=26e27f1173c859d3f455f4437f1f4e7a 280w, https://mintcdn.com/langdock-34/oaofNJPqDWePET7M/images/miro_custom_oauth_client.png?w=560\u0026fit=max\u0026auto=format\u0026n=oaofNJPqDWePET7M\u0026q=85\u0026s=6f1f387ef7e1bb8808873ae96479a2e9 560w, https://mintcdn.com/langdock-34/oaofNJPqDWePET7M/images/miro_custom_oauth_client.png?w=840\u0026fit=max\u0026auto=format\u0026n=oaofNJPqDWePET7M\u0026q=85\u0026s=b521b2a31db33cd823b5794ac3e1ba63 840w, https://mintcdn.com/langdock-34/oaofNJPqDWePET7M/images/miro_custom_oauth_client.png?w=1100\u0026fit=max\u0026auto=format\u0026n=oaofNJPqDWePET7M\u0026q=85\u0026s=ce4b3496c6f60f2ec61d17f3f24cf204 1100w, https://mintcdn.com/langdock-34/oaofNJPqDWePET7M/images/miro_custom_oauth_client.png?w=1650\u0026fit=max\u0026auto=format\u0026n=oaofNJPqDWePET7M\u0026q=85\u0026s=eacac09ddad47a8043a560610fad1d5f 1650w, https://mintcdn.com/langdock-34/oaofNJPqDWePET7M/images/miro_custom_oauth_client.png?w=2500\u0026fit=max\u0026auto=format\u0026n=oaofNJPqDWePET7M\u0026q=85\u0026s=bd3a55bbe15c49d8fa6a08dbac3520ad 2500w`})})]}),_jsxs(Step,{title:`Connect the app with Langdock`,children:[_jsxs(_components.p,{children:[`Add the `,_jsx(_components.strong,{children:`Redirect URL`}),` from Langdock’s Miro integration settings as a redirect URI in your Miro app, then enable every permission listed under `,_jsx(_components.strong,{children:`Scopes`}),` in the Miro app. Miro applies the permissions configured in the app rather than requesting them during authorization.`]}),_jsxs(_components.p,{children:[`Enter the `,_jsx(_components.strong,{children:`Client ID`}),` and `,_jsx(_components.strong,{children:`Client secret`}),` from your Miro app in Langdock as described in `,_jsx(_components.a,{href:`#how-custom-oauth-works`,children:`How Custom OAuth Works`}),`.`]})]})]})]}),`\n`,_jsx(_components.hr,{}),`\n`,_jsx(Heading,{level:`2`,id:`integrations-requiring-your-own-oauth-client`,children:`Integrations Requiring Your Own OAuth Client`}),`\n`,_jsx(_components.p,{children:`Some of our integrations can only be used when providing your own OAuth client. Details on how to connect them with Langdock are described in this section.`}),`\n`,_jsx(Heading,{level:`3`,id:`uipath`,children:`UiPath`}),`\n`,_jsx(_components.p,{children:`UiPath has no Langdock-managed OAuth client. External applications are registered per Automation Cloud organization, so a UiPath admin must create a confidential application in your organization before users can connect Orchestrator.`}),`\n`,_jsxs(Expandable,{title:`how to configure a UiPath OAuth client`,collapsible:true,children:[_jsx(_components.p,{children:_jsx(_components.strong,{children:`In UiPath`})}),_jsxs(_components.ol,{children:[`\n`,_jsxs(_components.li,{children:[`Open organization `,_jsx(_components.strong,{children:`Admin → External applications → OAuth apps`}),`.`]}),`\n`,_jsxs(_components.li,{children:[`Click `,_jsx(_components.strong,{children:`Add application`}),` and choose `,_jsx(_components.strong,{children:`Confidential application`}),`.`]}),`\n`,_jsxs(_components.li,{children:[`Under `,_jsx(_components.strong,{children:`Orchestrator`}),`, grant the scopes shown in Langdock on `,_jsx(_components.strong,{children:`User Scope(s)`}),` only. Leave `,_jsx(_components.strong,{children:`Application Scope(s)`}),` empty.`]}),`\n`,_jsxs(_components.li,{children:[`Paste the Langdock `,_jsx(_components.strong,{children:`Redirect URL`}),`, then save.`]}),`\n`,_jsxs(_components.li,{children:[`Copy the `,_jsx(_components.strong,{children:`Application ID`}),` and `,_jsx(_components.strong,{children:`app secret`}),`.`]}),`\n`]}),_jsx(_components.p,{children:_jsx(_components.strong,{children:`In Langdock`})}),_jsxs(_components.ol,{children:[`\n`,_jsxs(_components.li,{children:[`Open `,_jsx(_components.strong,{children:`UiPath`}),` under `,_jsx(_components.a,{href:`https://app.langdock.com/settings/workspace/products/integrations`,children:`Workspace settings → Integrations`}),`.`]}),`\n`,_jsxs(_components.li,{children:[`Click `,_jsx(_components.strong,{children:`Configure your OAuth client to use this integration.`})]}),`\n`,_jsx(_components.li,{children:`Paste the Application ID and app secret, save, and activate the client.`}),`\n`]}),_jsx(_components.p,{children:_jsx(_components.strong,{children:`Required authentication fields`})}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`UiPath Cloud URL`}),` (organization and tenant)`]}),`\n`]}),_jsxs(_components.p,{children:[`Save `,_jsx(_components.strong,{children:`UiPath Cloud URL`}),` as a workspace default in `,_jsx(_components.strong,{children:`OAuth connection details`}),`, for example `,_jsx(_components.code,{children:`https://cloud.uipath.com/acme/DefaultTenant/orchestrator_/`}),`. If you leave it empty, the connecting member pastes a URL like that, or enters `,_jsx(_components.code,{children:`org`}),` / `,_jsx(_components.code,{children:`org/tenant`}),`. Langdock runs a user-delegated OAuth flow with that user’s Orchestrator permissions.`]}),_jsx(_components.p,{children:_jsx(_components.strong,{children:`Full guides`})}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.a,{href:`/en/admin/manage-integrations/integration-setup-guides/uipath`,children:`UiPath setup guide`}),` (Langdock walkthrough)`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.a,{href:`https://docs.uipath.com/automation-cloud/automation-cloud/latest/admin-guide/authorizing-external-applications`,children:`UiPath OAuth apps overview`}),` (confidential apps and user scopes)`]}),`\n`]}),_jsx(Heading,{level:`3`,id:`uipath-integration-requirements`,children:`UiPath Integration Requirements`}),_jsxs(AccordionGroup,{children:[_jsx(Accordion,{title:`Are self-hosted or cloud-hosted accounts supported?`,id:`are-self-hosted-or-cloud-hosted-accounts-supported`,children:_jsx(_components.p,{children:`Only UiPath Automation Cloud. Automation Suite and other self-hosted hosts are not supported.`})}),_jsx(Accordion,{title:`Why is there no Langdock-managed OAuth client?`,id:`why-is-there-no-langdock-managed-oauth-client`,children:_jsx(_components.p,{children:`External OAuth apps are registered per UiPath organization. A client from one organization cannot cover every Langdock customer, so each organization creates its own confidential application.`})}),_jsxs(Accordion,{title:`Are any special account permissions / roles required?`,id:`are-any-special-account-permissions-roles-required`,children:[_jsx(_components.p,{children:`Yes.`}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`A UiPath admin creates the external application.`}),`\n`,_jsxs(_components.li,{children:[`Scopes go under `,_jsx(_components.strong,{children:`User Scope(s)`}),` for Orchestrator, not Application Scope(s).`]}),`\n`,_jsx(_components.li,{children:`Connecting users need Orchestrator access to the folders and processes they use in Langdock.`}),`\n`]})]}),_jsxs(Accordion,{title:`What about UiPath Automation Hub?`,id:`what-about-uipath-automation-hub`,children:[_jsx(_components.p,{children:`Separate integration. It uses an Open API token (API key), not this OAuth client.`}),_jsxs(_components.p,{children:[`See the `,_jsx(_components.a,{href:`/en/admin/manage-integrations/integration-setup-guides/uipath#uipath-automation-hub`,children:`UiPath setup guide`}),` for token setup and least-privilege guidance.`]})]})]})]}),`\n`,_jsx(Heading,{level:`3`,id:`servicenow`,children:`ServiceNow`}),`\n`,_jsxs(Expandable,{title:`how to configure a ServiceNow OAuth client`,collapsible:true,children:[_jsxs(_components.p,{children:[`To enable this integration for your workspace, your ServiceNow system administrator must create an OAuth client, in the form of an application registry in ServiceNow, following `,_jsx(_components.a,{href:`https://www.servicenow.com/docs/r/xanadu/security-management/security-incident-response/configure-application-registry-splunk.html?contentId=CHQRQznfzOrL_mxxa8MoCA`,children:`this`}),` documentation.`]}),_jsxs(_components.p,{children:[_jsx(_components.br,{}),`\n`,_jsx(_components.strong,{children:`Required authentication fields`})]}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Provide ServiceNow Subdomain`}),`\n`]}),_jsxs(_components.p,{children:[`Save the ServiceNow subdomain as a workspace default in `,_jsx(_components.strong,{children:`OAuth connection details`}),`. If you leave it empty, members enter it when they connect.`]}),_jsx(Heading,{level:`3`,id:`servicenow-integration-requirements`,children:`ServiceNow Integration Requirements`}),_jsxs(AccordionGroup,{children:[_jsx(Accordion,{title:`Are self-hosted or cloud-hosted accounts supported?`,id:`are-self-hosted-or-cloud-hosted-accounts-supported-1`,children:_jsx(_components.p,{children:`Only Cloud-hosted accounts are currently supported.`})}),_jsx(Accordion,{title:`Is a paid ServiceNow plan required?`,id:`is-a-paid-servicenow-plan-required`,children:_jsxs(_components.p,{children:[`A paid ServiceNow account is required to create an application registry.\\xA0View ServiceNow’s plans `,_jsx(_components.a,{href:`https://www.servicenow.com/lpgp/pricing.html?campid=107977\u0026cid=p:all:dg:b:prsp:exa:Google_CoreBrand_Top_Restructure:latam:mx\u0026ds_c=GOOG_LATAM_MX_ES_DEMANDGEN_ALBU_PRSP_Brand_EXA_Top-RES\u0026cmcid=71700000102193357\u0026ds_ag=Servicenow+Pricing_EXA_EN\u0026cmpid=58700008155106586\u0026ds_kids=p74103339564`,children:`here`}),`.`]})}),_jsx(Accordion,{title:`Are any special account permissions / roles required?`,id:`are-any-special-account-permissions-roles-required-1`,children:_jsxs(_components.p,{children:[`Yes. To connect by OAuth, your systems administrator should set up the right configuration within your instance to connect any user using an OAuth connection. E.g. all users need the\\xA0oauth_user role to be able to connect.\\xA0 Learn more about ServiceNow’s `,_jsx(_components.a,{href:`https://www.servicenow.com/docs/bundle/zurich-platform-security/page/integrate/identity/task/view-permissions-for-a-group.html`,children:`groups and permissions`})]})}),_jsx(Accordion,{title:`Are there usage limits?`,id:`are-there-usage-limits`,children:_jsxs(_components.p,{children:[`Yes. ServiceNow implements rate limiting to prevent excessive API usage. System administrators can configure rules that restrict the number of inbound REST API requests processed per hour. Learn more about ServiceNow’s `,_jsx(_components.a,{href:`https://www.servicenow.com/docs/bundle/zurich-api-reference/page/integrate/inbound-rest/concept/inbound-REST-API-rate-limiting.html`,children:`usage limits`}),`.`]})})]})]}),`\n`,_jsx(Heading,{level:`3`,id:`shopify-admin`,children:`Shopify Admin`}),`\n`,_jsxs(_components.p,{children:[`Shopify Admin has no Langdock managed OAuth app. A workspace admin creates an app in the Shopify Dev Dashboard and pastes the Client ID and Client Secret into Langdock. Connections use `,_jsx(_components.a,{href:`/en/using-langdock/integrations/connections#custom-scopes-and-application-level-permissions`,children:`application-level permissions`}),`: Langdock acts with the app’s Admin API scopes, not the personal Shopify role of the person who installed it.`]}),`\n`,_jsxs(Expandable,{title:`how to configure a Shopify Admin OAuth client`,collapsible:true,children:[_jsxs(_components.p,{children:[`Follow the full walkthrough in the `,_jsx(_components.a,{href:`/en/admin/manage-integrations/integration-setup-guides/shopify`,children:`Shopify Admin setup guide`}),`.`]}),_jsx(_components.p,{children:_jsx(_components.strong,{children:`Required authentication fields`})}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[`Store domain (a custom domain, a `,_jsx(_components.code,{children:`*.myshopify.com`}),` domain, or the store handle)`]}),`\n`]}),_jsxs(_components.p,{children:[`Save the store domain as a workspace default in `,_jsx(_components.strong,{children:`OAuth connection details`}),`, for example `,_jsx(_components.code,{children:`acme-store.myshopify.com`}),`. If you leave it empty, members enter it when they connect.`]}),_jsx(_components.p,{children:_jsx(_components.strong,{children:`Copy from Langdock into the Shopify app`})}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Redirect URL from the Shopify Admin OAuth client dialog`}),`\n`,_jsx(_components.li,{children:`Admin API scopes shown in that dialog (or the full list in the setup guide)`}),`\n`]}),_jsx(_components.p,{children:_jsx(_components.strong,{children:`Copy from Shopify into Langdock`})}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Client ID`}),`\n`,_jsx(_components.li,{children:`Client secret`}),`\n`]})]}),`\n`,_jsx(Heading,{level:`3`,id:`snowflake`,children:`Snowflake`}),`\n`,_jsx(_components.p,{children:`Configuring your own OAuth client for Snowflake gives you control over authentication policies, token validity periods, and IP allowlisting within your Snowflake environment.`}),`\n`,_jsxs(Expandable,{title:`how to configure a Snowflake OAuth client`,collapsible:true,children:[_jsx(_components.p,{children:_jsx(_components.strong,{children:`Required Information:`})}),_jsxs(_components.ul,{children:[`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`OAuth Redirect URL`}),`: Copy this from Langdock’s Snowflake integration settings page`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Client ID`}),`: Generated by Snowflake after creating the security integration`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Client Secret`}),`: Generated by Snowflake after creating the security integration`]}),`\n`,_jsxs(_components.li,{children:[_jsx(_components.strong,{children:`Authorization URL`}),`: Your Snowflake account’s authorization endpoint`]}),`\n`]}),_jsx(_components.p,{children:`The Redirect URL from Langdock must be provided in Snowflake, while the Client ID, Client Secret, and Authorization URL from Snowflake must be entered into Langdock’s integration settings.`}),_jsx(Note,{children:_jsxs(_components.p,{children:[`If your Snowflake account has network policies or IP allowlisting enabled, you may need to whitelist Langdock’s static IP address to allow connections. See `,_jsx(_components.a,{href:`/en/admin/security/static-ip-configuration`,children:`Static IP Configuration`}),` for details.`]})}),_jsx(Heading,{level:`3`,id:`setup-guide`,children:`Setup Guide`}),_jsxs(Steps,{children:[_jsxs(Step,{title:`Create Integration in Langdock`,children:[_jsx(_components.p,{children:`In your Langdock workspace, create your new Snowflake integration, and set up a custom OAuth Client.`}),_jsx(Expandable,{title:`how to set up a custom OAuth client in Langdock`,collapsible:true,children:_jsxs(_components.ol,{children:[`\n`,_jsxs(_components.li,{children:[`Open `,_jsx(_components.strong,{children:`Plugins`})]}),`\n`,_jsxs(_components.li,{children:[`Click `,_jsx(_components.strong,{children:`Create`}),`. If a menu opens, choose `,_jsx(_components.strong,{children:`Integration`}),`. In `,_jsx(_components.strong,{children:`Add integration`}),`, keep `,_jsx(_components.strong,{children:`Build integration from scratch`}),` selected.`]}),`\n`,_jsx(_components.li,{children:`Fill in your preferred name and description for your new Snowflake integration`}),`\n`,_jsx(_components.li,{children:`Click “Create”`}),`\n`,_jsx(_components.li,{children:`Authentication Type: Select “OAuth 2.0” from the dropdown`}),`\n`,_jsx(_components.li,{children:`Authentication fields: Leave blank`}),`\n`,_jsxs(_components.li,{children:[`OAuth Configuration: Save your `,_jsx(_components.strong,{children:`OAuth Redirect URL`})]}),`\n`]})})]}),_jsxs(Step,{title:`Create Security Integration in Snowflake`,children:[_jsx(_components.p,{children:`In Snowflake, select your workspace, and create a new security integration.`}),_jsxs(Expandable,{title:`how to create a new security integration in Snowflake`,collapsible:true,children:[_jsxs(_components.ol,{children:[`\n`,_jsxs(_components.li,{children:[`Create a new `,_jsx(_components.code,{children:`.sql`}),` file, and paste the following query:`]}),`\n`]}),_jsx(CodeBlock,{filename:``,numberOfLines:`8`,language:`sql`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`sql`,children:_jsxs(_components.code,{language:`sql`,numberOfLines:`8`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#569CD6`},children:`CREATE`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#569CD6`},children:` SECURITY`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` INTEGRATION `}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`\u003c`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`integration_name`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`>`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#569CD6`},children:` TYPE`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:` =`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` OAUTH`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#569CD6`},children:` ENABLED`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:` =`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` TRUE`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` OAUTH_CLIENT `}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` CUSTOM`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` OAUTH_CLIENT_TYPE `}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` CONFIDENTIAL`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` OAUTH_REDIRECT_URI `}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:` '\u003cyour_redirect_uri>'`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` OAUTH_ISSUE_REFRESH_TOKENS `}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` TRUE`})]}),`\n`,_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:` OAUTH_REFRESH_TOKEN_VALIDITY `}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#D4D4D4`},children:`=`}),_jsx(_components.span,{style:{color:`#0550AE`,\"--shiki-dark\":`#B5CEA8`},children:` 86400`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`;`})]}),`\n`]})})}),_jsxs(_components.ol,{start:`2`,children:[`\n`,_jsxs(_components.li,{children:[`Replace `,_jsx(_components.code,{children:`\u003cintegration_name>`}),` with a descriptive name and `,_jsx(_components.code,{children:`\u003cyour_redirect_uri>`}),` with the `,_jsx(_components.strong,{children:`OAuth Redirect URL`}),` from Step 1.`]}),`\n`,_jsxs(_components.li,{children:[`Run the query to create your new security integration in Snowflake.\n`,_jsx(_components.strong,{children:`Note:`}),` Adjust your `,_jsx(_components.code,{children:`OAUTH_REFRESH_TOKEN_VALIDITY`}),` value based on your security policies.`]}),`\n`]})]})]}),_jsx(Step,{title:`Retrieve Client ID and Client Secret`,children:_jsxs(Expandable,{title:`how to retrieve your Client ID, and Secret from Snowflake`,collapsible:true,children:[_jsxs(_components.ol,{children:[`\n`,_jsx(_components.li,{children:`Within the same workspace, run the following query:`}),`\n`]}),_jsx(CodeBlock,{filename:``,numberOfLines:`1`,language:`sql`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`sql`,children:_jsxs(_components.code,{language:`sql`,numberOfLines:`1`,children:[_jsxs(_components.span,{className:`line`,children:[_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#569CD6`},children:`SELECT`}),_jsx(_components.span,{style:{color:`#CF222E`,\"--shiki-dark\":`#569CD6`},children:` SYSTEM`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`$SHOW_OAUTH_CLIENT_SECRETS(`}),_jsx(_components.span,{style:{color:`#0A3069`,\"--shiki-dark\":`#CE9178`},children:`'\u003cintegration_name>'`}),_jsx(_components.span,{style:{color:`#1F2328`,\"--shiki-dark\":`#D4D4D4`},children:`);`})]}),`\n`]})})}),_jsxs(_components.ol,{start:`2`,children:[`\n`,_jsxs(_components.li,{children:[`Replace `,_jsx(_components.code,{children:`\u003cintegration_name>`}),` with the name you gave your security integration in the previous step.`]}),`\n`,_jsxs(_components.li,{children:[`Save your `,_jsx(_components.strong,{children:`Client ID`}),` and `,_jsx(_components.strong,{children:`Client Secret`}),`. Store these credentials securely as they provide access to your Snowflake account.`]}),`\n`]})]})}),_jsx(Step,{title:`Retrieve Account URL from Snowflake`,children:_jsx(Expandable,{title:`how to retrieve your Account URL from Snowflake`,collapsible:true,children:_jsxs(_components.ol,{children:[`\n`,_jsx(_components.li,{children:`Click on your account name in the bottom left corner of your Snowflake application`}),`\n`,_jsx(_components.li,{children:`Under the Account Section, click on “View Account Details”`}),`\n`,_jsxs(_components.li,{children:[`Copy your `,_jsx(_components.strong,{children:`Account URL`})]}),`\n`]})})}),_jsx(Step,{title:`Configure Integration Settings in Langdock`,children:_jsxs(Expandable,{title:`how to configure your Snowflake OAuth client in Langdock `,collapsible:true,children:[_jsxs(_components.ol,{children:[`\n`,_jsxs(_components.li,{children:[`\n`,_jsxs(_components.p,{children:[`Add your `,_jsx(_components.strong,{children:`Client ID`}),` and `,_jsx(_components.strong,{children:`Client Secret`}),` from Step 3 in the respective input fields of your new Langdock integration`]}),`\n`]}),`\n`,_jsxs(_components.li,{children:[`\n`,_jsx(_components.p,{children:`In the following sections:`}),`\n`,_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`Authorization URL`}),`\n`,_jsx(_components.li,{children:`Access Token URL`}),`\n`,_jsx(_components.li,{children:`Refresh Token URL`}),`\n`]}),`\n`,_jsxs(_components.p,{children:[`Replace only `,_jsx(_components.code,{children:`https://example.com`}),` with your `,_jsx(_components.strong,{children:`Snowflake Account URL`}),` from Step 4.`]}),`\n`]}),`\n`]}),_jsx(_components.p,{children:`Example:`}),_jsx(CodeBlock,{numberOfLines:`2`,language:`text`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`text`,children:_jsxs(_components.code,{language:`text`,numberOfLines:`2`,children:[_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:`https://example.com/oauth/authorize`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{})})]})})}),_jsx(_components.p,{children:`Becomes:`}),_jsx(CodeBlock,{numberOfLines:`2`,language:`text`,children:_jsx(_components.pre,{className:`shiki shiki-themes github-light-default dark-plus`,style:{backgroundColor:`#ffffff`,\"--shiki-dark-bg\":`#0B0C0E`,color:`#1f2328`,\"--shiki-dark\":`#D4D4D4`},language:`text`,children:_jsxs(_components.code,{language:`text`,numberOfLines:`2`,children:[_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{children:`https://\u003cyour-snowflake-account-url>/oauth/authorize`})}),`\n`,_jsx(_components.span,{className:`line`,children:_jsx(_components.span,{})})]})})}),_jsxs(_components.ol,{start:`3`,children:[`\n`,_jsxs(_components.li,{children:[`Leave `,_jsx(_components.strong,{children:`Scopes`}),` empty.`]}),`\n`,_jsxs(_components.li,{children:[`Click `,_jsx(_components.strong,{children:`Save`})]}),`\n`]}),_jsx(Note,{children:_jsxs(_components.p,{children:[`Snowflake OAuth uses roles rather than scopes. Leave `,_jsx(_components.strong,{children:`Scopes`}),` empty so each connecting user gets their default Snowflake role. If you enter a session role such as `,_jsx(_components.code,{children:`session:role:SYSADMIN`}),`, every user authenticates against that role. Users who do not have it in Snowflake cannot connect.`]})})]})}),_jsx(Step,{title:`Test the Connection`,children:_jsxs(Expandable,{title:`how to add a Connection to your Snowflake Integration`,collapsible:true,children:[_jsx(_components.p,{children:`Click “Add Connection” in your Snowflake integration.`}),_jsxs(_components.ul,{children:[`\n`,_jsx(_components.li,{children:`You should be directed to the Snowflake Authorization screen`}),`\n`,_jsx(_components.li,{children:`Log into your Snowflake account`}),`\n`]}),_jsx(_components.p,{children:`You have now successfully set up your own OAuth Snowflake integration!`})]})})]})]})]})}function MDXContent(props={}){const{wrapper:MDXLayout}={..._provideComponents(),...props.components};return MDXLayout?_jsx(MDXLayout,{...props,children:_jsx(_createMdxContent,{...props})}):_createMdxContent(props)}return{default:MDXContent};function _missingMdxReference(id,component){throw new Error(`Expected `+(component?`component`:`object`)+\" `\"+id+\"` to be defined: you likely forgot to import, pass, or provide it.\")}","frontmatter":{},"scope":{"config":{},"pageMetadata":{"title":"Bring Your Own OAuth Client","sidebarTitle":"Bring Your Own OAuth Client","description":"Set up custom OAuth applications for integrations, assign clients to your workspace or user groups, and control scopes, tenant policies, and branding.","keywords":["oauth","authentication","integrations","custom client","user groups","security","branding"],"href":"/en/admin/manage-integrations/bring-your-own-oauth"}}},"mdxSourceWithNoJs":null},"mdxExtracts":{"tableOfContents":[{"title":"How Custom OAuth Works","slug":"how-custom-oauth-works","depth":2,"children":[]},{"title":"Assign OAuth Clients to User Groups","slug":"assign-oauth-clients-to-user-groups","depth":2,"children":[]},{"title":"Integration Settings Interface","slug":"integration-settings-interface","depth":2,"children":[]},{"title":"OAuth connection details","slug":"additional-parameters","depth":2,"children":[]},{"title":"Manage Custom OAuth Clients","slug":"manage-custom-oauth-clients","depth":2,"children":[]},{"title":"Common Configuration Errors","slug":"common-configuration-errors","depth":2,"children":[]},{"title":"Custom Miro OAuth Client","slug":"custom-miro-oauth-client","depth":2,"children":[]},{"title":"Integrations Requiring Your Own OAuth Client","slug":"integrations-requiring-your-own-oauth-client","depth":2,"children":[{"title":"UiPath","slug":"uipath","depth":3,"children":[]},{"title":"ServiceNow","slug":"servicenow","depth":3,"children":[]},{"title":"Shopify Admin","slug":"shopify-admin","depth":3,"children":[]},{"title":"Snowflake","slug":"snowflake","depth":3,"children":[]}]}],"codeExamples":{}},"jsLinks":[],"subdomain":"langdock-34","siteName":"Docs","title":"Bring Your Own OAuth Client - Docs","navMaps":{"firstHrefInVersion":{},"firstHrefInLanguage":{"en":{"href":"/en/admin/manage-integrations/bring-your-own-oauth","matchLevel":0},"de":{"href":"/de/admin/manage-integrations/bring-your-own-oauth","matchLevel":1}}},"lastModified":"2026-10-28T13:39:39.094Z","originalFileLocation":"en/admin/manage-integrations/bring-your-own-oauth.mdx","locale":"en"},"headHtml":"\u003cscript data-mint-head>(function(){var d=document.documentElement,p=null;if(!p){try{p=localStorage.getItem(\"isDarkMode\")}catch(e){}if(p==='true')p='dark';else if(p==='false')p='light';if(p!=='light'\u0026\u0026p!=='dark'\u0026\u0026p!=='system')p=\"system\"}var r=p==='system'?(matchMedia(\"(prefers-color-scheme: dark)\").matches?'dark':'light'):p;d.classList.remove(r==='dark'?'light':'dark');d.classList.add(r);d.setAttribute(\"data-theme-preference\",p)})();\u003c/script>\u003cmeta data-mint-head name=\"description\" content=\"Set up custom OAuth applications for integrations, assign clients to your workspace or user groups, and control scopes, tenant policies, and branding.\">\u003cmeta data-mint-head name=\"application-name\" content=\"Docs\">\u003cmeta data-mint-head name=\"generator\" content=\"Mintlify\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/mintlify-assets/_mintlify/favicons/langdock-34/8EMNQyrrZlRONhj1/_generated/favicon/android-chrome-192x192.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"apple-touch-icon\" type=\"image/png\" sizes=\"180x180\" href=\"/mintlify-assets/_mintlify/favicons/langdock-34/8EMNQyrrZlRONhj1/_generated/favicon/apple-touch-icon.png\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/mintlify-assets/_mintlify/favicons/langdock-34/8EMNQyrrZlRONhj1/_generated/favicon/favicon-16x16.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/mintlify-assets/_mintlify/favicons/langdock-34/8EMNQyrrZlRONhj1/_generated/favicon/favicon-32x32.png\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/mintlify-assets/_mintlify/favicons/langdock-34/8EMNQyrrZlRONhj1/_generated/favicon/favicon.ico\" media=\"(prefers-color-scheme: light)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"192x192\" href=\"/mintlify-assets/_mintlify/favicons/langdock-34/8EMNQyrrZlRONhj1/_generated/favicon-dark/android-chrome-192x192.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"16x16\" href=\"/mintlify-assets/_mintlify/favicons/langdock-34/8EMNQyrrZlRONhj1/_generated/favicon-dark/favicon-16x16.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"icon\" type=\"image/png\" sizes=\"32x32\" href=\"/mintlify-assets/_mintlify/favicons/langdock-34/8EMNQyrrZlRONhj1/_generated/favicon-dark/favicon-32x32.png\" media=\"(prefers-color-scheme: dark)\">\u003clink data-mint-head rel=\"shortcut icon\" type=\"image/x-icon\" href=\"/mintlify-assets/_mintlify/favicons/langdock-34/8EMNQyrrZlRONhj1/_generated/favicon-dark/favicon.ico\" media=\"(prefers-color-scheme: dark)\">\u003cmeta data-mint-head property=\"og:title\" content=\"Bring Your Own OAuth Client - Docs\">\u003cmeta data-mint-head property=\"og:description\" content=\"Set up custom OAuth applications for integrations, assign clients to your workspace or user groups, and control scopes, tenant policies, and branding.\">\u003cmeta data-mint-head property=\"og:site_name\" content=\"Docs\">\u003cmeta data-mint-head property=\"og:url\" content=\"https://docs.langdock.com/en/admin/manage-integrations/bring-your-own-oauth\">\u003cmeta data-mint-head property=\"og:type\" content=\"website\">\u003cmeta data-mint-head property=\"og:image\" content=\"https://langdock-34.mintlify.site/_mintlify/api/og/v2?division=Manage+Integrations\u0026amp;title=Bring+Your+Own+OAuth+Client\u0026amp;description=Set+up+custom+OAuth+applications+for+integrations%2C+assign+clients+to+your+workspace+or+user+groups%2C+and+control+scopes%2C+tenant+policies%2C+and+branding.\u0026amp;theme=c0a8a64be653b2c8cdece0f0\u0026amp;signature=b8840bda8b6c20216c429f57dcd80cc44c37b36c2c7e768449cd2b4b78edcd8d\">\u003cmeta data-mint-head property=\"og:image:width\" content=\"1200\">\u003cmeta data-mint-head property=\"og:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"twitter:card\" content=\"summary_large_image\">\u003cmeta data-mint-head name=\"twitter:title\" content=\"Bring Your Own OAuth Client - Docs\">\u003cmeta data-mint-head name=\"twitter:description\" content=\"Set up custom OAuth applications for integrations, assign clients to your workspace or user groups, and control scopes, tenant policies, and branding.\">\u003cmeta data-mint-head name=\"twitter:image\" content=\"https://langdock-34.mintlify.site/_mintlify/api/og/v2?division=Manage+Integrations\u0026amp;title=Bring+Your+Own+OAuth+Client\u0026amp;description=Set+up+custom+OAuth+applications+for+integrations%2C+assign+clients+to+your+workspace+or+user+groups%2C+and+control+scopes%2C+tenant+policies%2C+and+branding.\u0026amp;theme=c0a8a64be653b2c8cdece0f0\u0026amp;signature=b8840bda8b6c20216c429f57dcd80cc44c37b36c2c7e768449cd2b4b78edcd8d\">\u003cmeta data-mint-head name=\"twitter:image:width\" content=\"1200\">\u003cmeta data-mint-head name=\"twitter:image:height\" content=\"630\">\u003cmeta data-mint-head name=\"msapplication-config\" content=\"/mintlify-assets/_mintlify/favicons/langdock-34/8EMNQyrrZlRONhj1/_generated/favicon/browserconfig.xml\">\u003cmeta data-mint-head name=\"apple-mobile-web-app-title\" content=\"Docs\">\u003cmeta data-mint-head name=\"msapplication-TileColor\" content=\"#4469FC\">\u003clink data-mint-head rel=\"canonical\" href=\"https://docs.langdock.com/en/admin/manage-integrations/bring-your-own-oauth\">\u003clink data-mint-head rel=\"alternate\" type=\"application/xml\" href=\"/sitemap.xml\">\u003clink data-mint-head rel=\"alternate\" type=\"text/markdown\" href=\"/en/admin/manage-integrations/bring-your-own-oauth.md\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"en\" href=\"https://docs.langdock.com/en/admin/manage-integrations/bring-your-own-oauth\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"de\" href=\"https://docs.langdock.com/de/admin/manage-integrations/bring-your-own-oauth\">\u003clink data-mint-head rel=\"alternate\" hreflang=\"x-default\" href=\"https://docs.langdock.com/en/admin/manage-integrations/bring-your-own-oauth\">\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@graph\":[{\"@type\":\"Organization\",\"@id\":\"https://docs.langdock.com/#organization\",\"name\":\"Docs\",\"url\":\"https://docs.langdock.com\",\"logo\":{\"@type\":\"ImageObject\",\"url\":\"https://mintcdn.com/langdock-34/URgvNwU7CYGZq8R7/logo/light.svg?fit=max\u0026auto=format\u0026n=URgvNwU7CYGZq8R7\u0026q=85\u0026s=594b4bd597e2629fb1a7dccfae6aa1c4\"}},{\"@type\":\"WebSite\",\"@id\":\"https://docs.langdock.com#website\",\"name\":\"Docs\",\"url\":\"https://docs.langdock.com\",\"publisher\":{\"@id\":\"https://docs.langdock.com/#organization\"}},{\"@type\":\"WebPage\",\"@id\":\"https://docs.langdock.com/en/admin/manage-integrations/bring-your-own-oauth#webpage\",\"url\":\"https://docs.langdock.com/en/admin/manage-integrations/bring-your-own-oauth\",\"name\":\"Bring Your Own OAuth Client\",\"description\":\"Set up custom OAuth applications for integrations, assign clients to your workspace or user groups, and control scopes, tenant policies, and branding.\",\"dateModified\":\"2026-10-28T13:39:39.094Z\",\"isPartOf\":{\"@id\":\"https://docs.langdock.com#website\"},\"breadcrumb\":{\"@id\":\"https://docs.langdock.com/en/admin/manage-integrations/bring-your-own-oauth#breadcrumb\"}},{\"@type\":\"BreadcrumbList\",\"@id\":\"https://docs.langdock.com/en/admin/manage-integrations/bring-your-own-oauth#breadcrumb\",\"itemListElement\":[{\"@type\":\"ListItem\",\"position\":1,\"name\":\"Manage Integrations\",\"item\":\"https://docs.langdock.com/en/admin/manage-integrations/integrations-guide\"},{\"@type\":\"ListItem\",\"position\":2,\"name\":\"Bring Your Own OAuth Client\",\"item\":\"https://docs.langdock.com/en/admin/manage-integrations/bring-your-own-oauth\"}]},{\"@type\":[\"Article\",\"TechArticle\"],\"@id\":\"https://docs.langdock.com/en/admin/manage-integrations/bring-your-own-oauth#article\",\"headline\":\"Bring Your Own OAuth Client\",\"name\":\"Bring Your Own OAuth Client\",\"description\":\"Set up custom OAuth applications for integrations, assign clients to your workspace or user groups, and control scopes, tenant policies, and branding.\",\"url\":\"https://docs.langdock.com/en/admin/manage-integrations/bring-your-own-oauth\",\"mainEntityOfPage\":{\"@id\":\"https://docs.langdock.com/en/admin/manage-integrations/bring-your-own-oauth#webpage\"},\"dateModified\":\"2026-10-28T13:39:39.094Z\",\"keywords\":\"oauth, authentication, integrations, custom client, user groups, security, branding\",\"publisher\":{\"@id\":\"https://docs.langdock.com/#organization\"},\"isPartOf\":{\"@id\":\"https://docs.langdock.com#website\"}}]}\u003c/script>\u003cscript data-mint-head type=\"application/ld+json\">{\"@context\":\"https://schema.org\",\"@type\":\"WebSite\",\"name\":\"Docs\",\"publisher\":{\"@type\":\"Organization\",\"name\":\"Docs\"},\"provider\":{\"@type\":\"Organization\",\"name\":\"Mintlify\",\"url\":\"https://mintlify.com\"}}\u003c/script>","agentPointerHref":"/en/admin/manage-integrations/bring-your-own-oauth.md","siteName":"Docs","nav":{"global":{"anchors":[{"anchor":"Changelog","icon":"newspaper","href":"https://www.langdock.com/changelog"},{"anchor":"Status","icon":"signal-bars","href":"https://status.langdock.com/"},{"anchor":"Support","icon":"messages-question","href":"https://www.langdock.com/contact-us"}]},"languages":[{"language":"en","default":true,"tabs":[{"tab":"Using Langdock","pages":[{"title":"Using Langdock","href":"/en/using-langdock/get-started/introduction"}]},{"tab":"Developer","pages":[{"title":"Developer","href":"/en/developer/overview/api-introduction"}]},{"tab":"Admin","groups":[{"group":"Workspace","pages":[{"title":"Workspace Settings","href":"/en/admin/workspace/workspace"},{"title":"Workspace Setup","href":"/en/admin/workspace/workspace-setup"},{"title":"Roles and extra permissions","href":"/en/admin/workspace/roles"},{"title":"Permission Recommendations","href":"/en/admin/workspace/permissions"},{"title":"Manage scheduled tasks","href":"/en/admin/workspace/scheduled-tasks"}]},{"group":"Manage Agents","pages":[{"title":"Allowed usage","href":"/en/admin/manage-agents/allowed-usage"},{"title":"Verify Agents","href":"/en/admin/manage-agents/verify-agents"},{"title":"Highlight Agents","href":"/en/admin/manage-agents/highlight-agents"},{"title":"Disable Agents","href":"/en/admin/manage-agents/disable-agents"},{"title":"Archive Agents","href":"/en/admin/manage-agents/archive-agents"},{"title":"Unassign Agents","href":"/en/admin/manage-agents/unassign-agents"},{"title":"Admin-managed sharing","href":"/en/admin/manage-agents/admin-managed-sharing"},{"title":"Agent limits","href":"/en/admin/manage-agents/agent-limits"}]},{"group":"Manage Workflows","pages":[{"title":"Best Practices","href":"/en/admin/manage-workflows/best-practices"},{"title":"Workflow limits","href":"/en/admin/manage-workflows/spend-limits"},{"title":"Security Controls","href":"/en/admin/manage-workflows/security-controls"}]},{"group":"Manage Meetings","pages":[{"title":"Access","href":"/en/admin/manage-meetings/access"},{"title":"Transparency","href":"/en/admin/manage-meetings/transparency"},{"title":"Data \u0026 sharing","href":"/en/admin/manage-meetings/data-sharing"}]},{"group":"Manage Apps","pages":[{"title":"Enable Apps","href":"/en/admin/manage-apps/enable-apps"},{"title":"Set Apps permissions","href":"/en/admin/manage-apps/permissions"},{"title":"Manage apps in Governance","href":"/en/admin/manage-apps/governance"},{"title":"Apps security and data access","sidebarTitle":"Security and data access","href":"/en/admin/manage-apps/security"}]},{"group":"Desktop app","pages":[{"title":"Enterprise Guide for Langdock Desktop","sidebarTitle":"Enterprise Guide for Langdock Desktop","href":"/en/admin/desktop-app/deploy"},{"title":"Upgrade an existing deployment","sidebarTitle":"Upgrade an existing deployment","href":"/en/admin/desktop-app/upgrade"},{"title":"Manage desktop app updates","sidebarTitle":"Manage updates","href":"/en/admin/desktop-app/updates"}]},{"group":"Manage Integrations","pages":[{"title":"Integrations Guide","href":"/en/admin/manage-integrations/integrations-guide"},{"group":"Hidden","hidden":true,"pages":[{"title":"Integration Details","href":"/en/admin/manage-integrations/integrations-details"}]},{"group":"Integration Setup Guides","pages":[{"title":"Ashby","href":"/en/admin/manage-integrations/integration-setup-guides/ashby"},{"title":"Azure AI Search","href":"/en/admin/manage-integrations/integration-setup-guides/azure-search"},{"title":"Databricks","href":"/en/admin/manage-integrations/integration-setup-guides/databricks"},{"title":"Google Maps","href":"/en/admin/manage-integrations/integration-setup-guides/google-maps"},{"title":"Looker","href":"/en/admin/manage-integrations/integration-setup-guides/looker"},{"title":"Luma","href":"/en/admin/manage-integrations/integration-setup-guides/luma"},{"title":"Metabase","href":"/en/admin/manage-integrations/integration-setup-guides/metabase"},{"group":"Microsoft Fabric","pages":[{"title":"Microsoft Fabric","sidebarTitle":"Overview","href":"/en/admin/manage-integrations/integration-setup-guides/microsoft-fabric"},{"title":"Configure Microsoft Fabric for Langdock","sidebarTitle":"Admin configuration","href":"/en/admin/manage-integrations/integration-setup-guides/microsoft-fabric/setup"},{"title":"Control access and mutations","sidebarTitle":"Access and mutations","href":"/en/admin/manage-integrations/integration-setup-guides/microsoft-fabric/permissions-and-mutations"},{"title":"Troubleshoot Microsoft Fabric","sidebarTitle":"Troubleshooting","href":"/en/admin/manage-integrations/integration-setup-guides/microsoft-fabric/troubleshooting"}]},{"title":"Microsoft Integrations: Permissions \u0026 Admin Approval","sidebarTitle":"Microsoft","href":"/en/admin/manage-integrations/integration-setup-guides/microsoft"},{"title":"Microsoft Entra","href":"/en/admin/manage-integrations/integration-setup-guides/microsoft-entra"},{"title":"ServiceNow","href":"/en/admin/manage-integrations/integration-setup-guides/service-now"},{"title":"Shopify Admin","href":"/en/admin/manage-integrations/integration-setup-guides/shopify"},{"title":"UiPath","href":"/en/admin/manage-integrations/integration-setup-guides/uipath"},{"title":"Zoom","description":"Connect Zoom to Langdock to manage meetings, access recordings, and retrieve transcripts from your conversations","href":"/en/admin/manage-integrations/integration-setup-guides/zoom"}]},{"title":"Bring Your Own OAuth Client","sidebarTitle":"Bring Your Own OAuth Client","href":"/en/admin/manage-integrations/bring-your-own-oauth"},{"title":"Sensitivity Label Policy","description":"Block Microsoft Purview sensitivity labels so SharePoint, OneDrive, Outlook, Teams, and Excel withhold files and messages your workspace should not process.","href":"/en/admin/manage-integrations/sensitivity-label-policy"},{"title":"Default tool stack","href":"/en/admin/manage-integrations/default-tool-stack"},{"title":"Manage Action Access","href":"/en/admin/manage-integrations/manage-action-access"},{"title":"Manage Action-Level Scopes","href":"/en/admin/manage-integrations/manage-action-level-scopes"},{"group":"Microsoft Integration Scopes","pages":[{"title":"Microsoft Integration Scopes","sidebarTitle":"Overview","href":"/en/admin/manage-integrations/microsoft-integration-scopes"},{"title":"Azure DevOps","href":"/en/admin/manage-integrations/microsoft-integration-scopes/azure-devops"},{"title":"Azure Resource Manager","href":"/en/admin/manage-integrations/microsoft-integration-scopes/azure-resource-manager"},{"title":"Microsoft Dynamics 365","href":"/en/admin/manage-integrations/microsoft-integration-scopes/dynamics-365"},{"title":"Microsoft Entra","href":"/en/admin/manage-integrations/microsoft-integration-scopes/entra"},{"title":"Microsoft Excel","href":"/en/admin/manage-integrations/microsoft-integration-scopes/excel"},{"title":"Microsoft Fabric","href":"/en/admin/manage-integrations/microsoft-integration-scopes/fabric"},{"title":"Microsoft OneDrive","href":"/en/admin/manage-integrations/microsoft-integration-scopes/onedrive"},{"title":"Microsoft Planner","href":"/en/admin/manage-integrations/microsoft-integration-scopes/planner"},{"title":"Microsoft Power BI","href":"/en/admin/manage-integrations/microsoft-integration-scopes/power-bi"},{"title":"Microsoft Teams","href":"/en/admin/manage-integrations/microsoft-integration-scopes/teams"},{"title":"Microsoft To Do","href":"/en/admin/manage-integrations/microsoft-integration-scopes/todo"},{"title":"Microsoft Viva Engage","href":"/en/admin/manage-integrations/microsoft-integration-scopes/viva-engage"},{"title":"Outlook Calendar","href":"/en/admin/manage-integrations/microsoft-integration-scopes/outlook-calendar"},{"title":"Outlook Email","href":"/en/admin/manage-integrations/microsoft-integration-scopes/outlook-email"},{"title":"SharePoint","href":"/en/admin/manage-integrations/microsoft-integration-scopes/sharepoint"}]},{"group":"Chatbot Setup Guides","pages":[{"title":"Slack Bot (Setup)","href":"/en/admin/manage-integrations/chatbot-setup-guides/slack"},{"title":"Teams Bot (Setup)","href":"/en/admin/manage-integrations/chatbot-setup-guides/teams-bot"}]},{"group":"Add-in Setup Guides","pages":[{"title":"Excel Add-in (Setup)","sidebarTitle":"Excel","href":"/en/admin/manage-integrations/add-in-setup-guides/excel"},{"title":"Outlook Add-in (Setup)","sidebarTitle":"Outlook","href":"/en/admin/manage-integrations/add-in-setup-guides/outlook"}]}]},{"group":"Manage Usage","pages":[{"title":"Business plans","href":"/en/admin/manage-usage/plans"},{"title":"Extra Usage","href":"/en/admin/manage-usage/extra-usage"},{"title":"Usage credits","href":"/en/admin/manage-usage/usage-credits"},{"title":"Personal API keys","href":"/en/admin/manage-usage/personal-api-keys"}]},{"group":"Bring your own Keys (BYOK)","pages":[{"title":"Overview","href":"/en/admin/byok/byok"},{"title":"Getting started","href":"/en/admin/byok/byok-setup"},{"title":"How to add your own models","href":"/en/admin/byok/adding-models"},{"title":"How to add fallback models","href":"/en/admin/byok/fallback-models"},{"title":"Recommended Models","href":"/en/admin/byok/recommended-models"},{"title":"Setup Guides","href":"/en/admin/byok/setup-guides"},{"title":"Attribute LiteLLM spend per user","href":"/en/admin/byok/litellm-user-attribution"},{"group":"Usage limits","pages":[{"title":"Usage and spend limits","href":"/en/admin/manage-usage/byok/usage-limits"},{"title":"How to migrate to cost-based limits","href":"/en/admin/manage-usage/byok/migration"}]}]},{"group":"Governance","pages":[{"title":"Overview","href":"/en/admin/governance/overview"},{"title":"Agents","href":"/en/admin/governance/agents"},{"title":"Skills","href":"/en/admin/governance/skills"},{"title":"Compliance Rules","href":"/en/admin/governance/compliance-rules"},{"title":"Share requests","href":"/en/admin/governance/share-requests"}]},{"group":"Compliance \u0026 Governance","pages":[{"title":"Usage Exports","href":"/en/admin/compliance-and-governance/usage-exports"},{"title":"API Usage Export","href":"/en/admin/compliance-and-governance/api-usage-export"},{"title":"Useful Links","href":"/en/admin/compliance-and-governance/legal-compliance"}]},{"group":"AI Adoption \u0026 Rollout","pages":[{"group":"Getting Started","pages":[{"title":"Get Started","href":"/en/admin/ai-adoption-and-rollout/getting-started/onboarding-guide"},{"title":"Rollout Setup","href":"/en/admin/ai-adoption-and-rollout/getting-started/rollout-setup"},{"title":"Rollout Playbook","href":"/en/admin/ai-adoption-and-rollout/getting-started/rollout-playbook"},{"title":"Identifying Use Cases","href":"/en/admin/ai-adoption-and-rollout/getting-started/identify-use-cases"}]},{"group":"Best Practices","pages":[{"title":"Tips and tricks for your internal channels","href":"/en/admin/ai-adoption-and-rollout/best-practices/tips-and-tricks-internal"},{"title":"API Key Best Practices","href":"/en/admin/ai-adoption-and-rollout/best-practices/api-key-best-practices"}]},{"group":"Technical Setup","pages":[{"title":"Shared Slack Channel","href":"/en/admin/ai-adoption-and-rollout/technical-setup/slack-channel"},{"title":"Shared Teams Channel","href":"/en/admin/ai-adoption-and-rollout/technical-setup/teams-channel"}]}]},{"group":"Security","pages":[{"title":"Static IP Configuration","href":"/en/admin/security/static-ip-configuration"},{"title":"IP Restrictions","href":"/en/admin/security/ip-restrictions"},{"title":"Session Management","href":"/en/admin/security/session-management"},{"title":"Mobile App and Microsoft Intune","href":"/en/admin/security/mobile-app-intune"},{"group":"SAML (SSO)","pages":[{"title":"Getting Started","href":"/en/admin/security/saml/saml"},{"title":"Microsoft Entra ID SAML Setup","href":"/en/admin/security/saml/entra"},{"title":"Google SAML Setup","href":"/en/admin/security/saml/google"},{"title":"Okta SAML Setup","href":"/en/admin/security/saml/okta"}]},{"group":"SCIM","pages":[{"title":"Getting Started","href":"/en/admin/security/scim/scim"},{"title":"Microsoft Entra ID Setup","href":"/en/admin/security/scim/entra"}]}]},{"group":"Billing","pages":[{"title":"Pricing","href":"/en/admin/billing/pricing"},{"title":"Subscription","href":"/en/admin/billing/subscription"},{"title":"Invoices","href":"/en/admin/billing/invoices"}]},{"group":"Product Updates","hidden":true,"pages":[{"title":"Release Notes","mode":"center","href":"/en/admin/release-notes"}]}]}]},{"language":"de","pages":[{"title":"de","href":"/de/admin/manage-integrations/bring-your-own-oauth"}]}]},"basePath":"","title":"Bring Your Own OAuth Client - Docs","buildId":"dpl_596ePT575z4qnAFksq1biRW97aLY","deploymentId":"dpl_596ePT575z4qnAFksq1biRW97aLY","dynamics":["07c022d89b","a74be98ba7"],"chunks":["Frame-BXrZabKK.js","DynamicMarkdown-CtasenyM.js","zoom-image-lightbox-C5F0mVLH.js","lightbox-handle-r17bVUz3.js"]}